Focus on your product. We run the FedRAMP program with you.
Every program starts on FedRAMP 20x, so you meet the CR26 deadlines on time. CIPHER GRC and dedicated Traverge experts carry your program. You stay the decision maker.


FedRAMP certifies. Agencies authorize.
Founder Jon Riddle on why certification is only the first door, and how CIPHER GRC gets you through the next one. Product screens show sample data for a fictional provider, Acme Inc.
See your whole FedRAMP program in one place
The screens your team works in every day, shown with sample data for a fictional provider, Acme Inc.
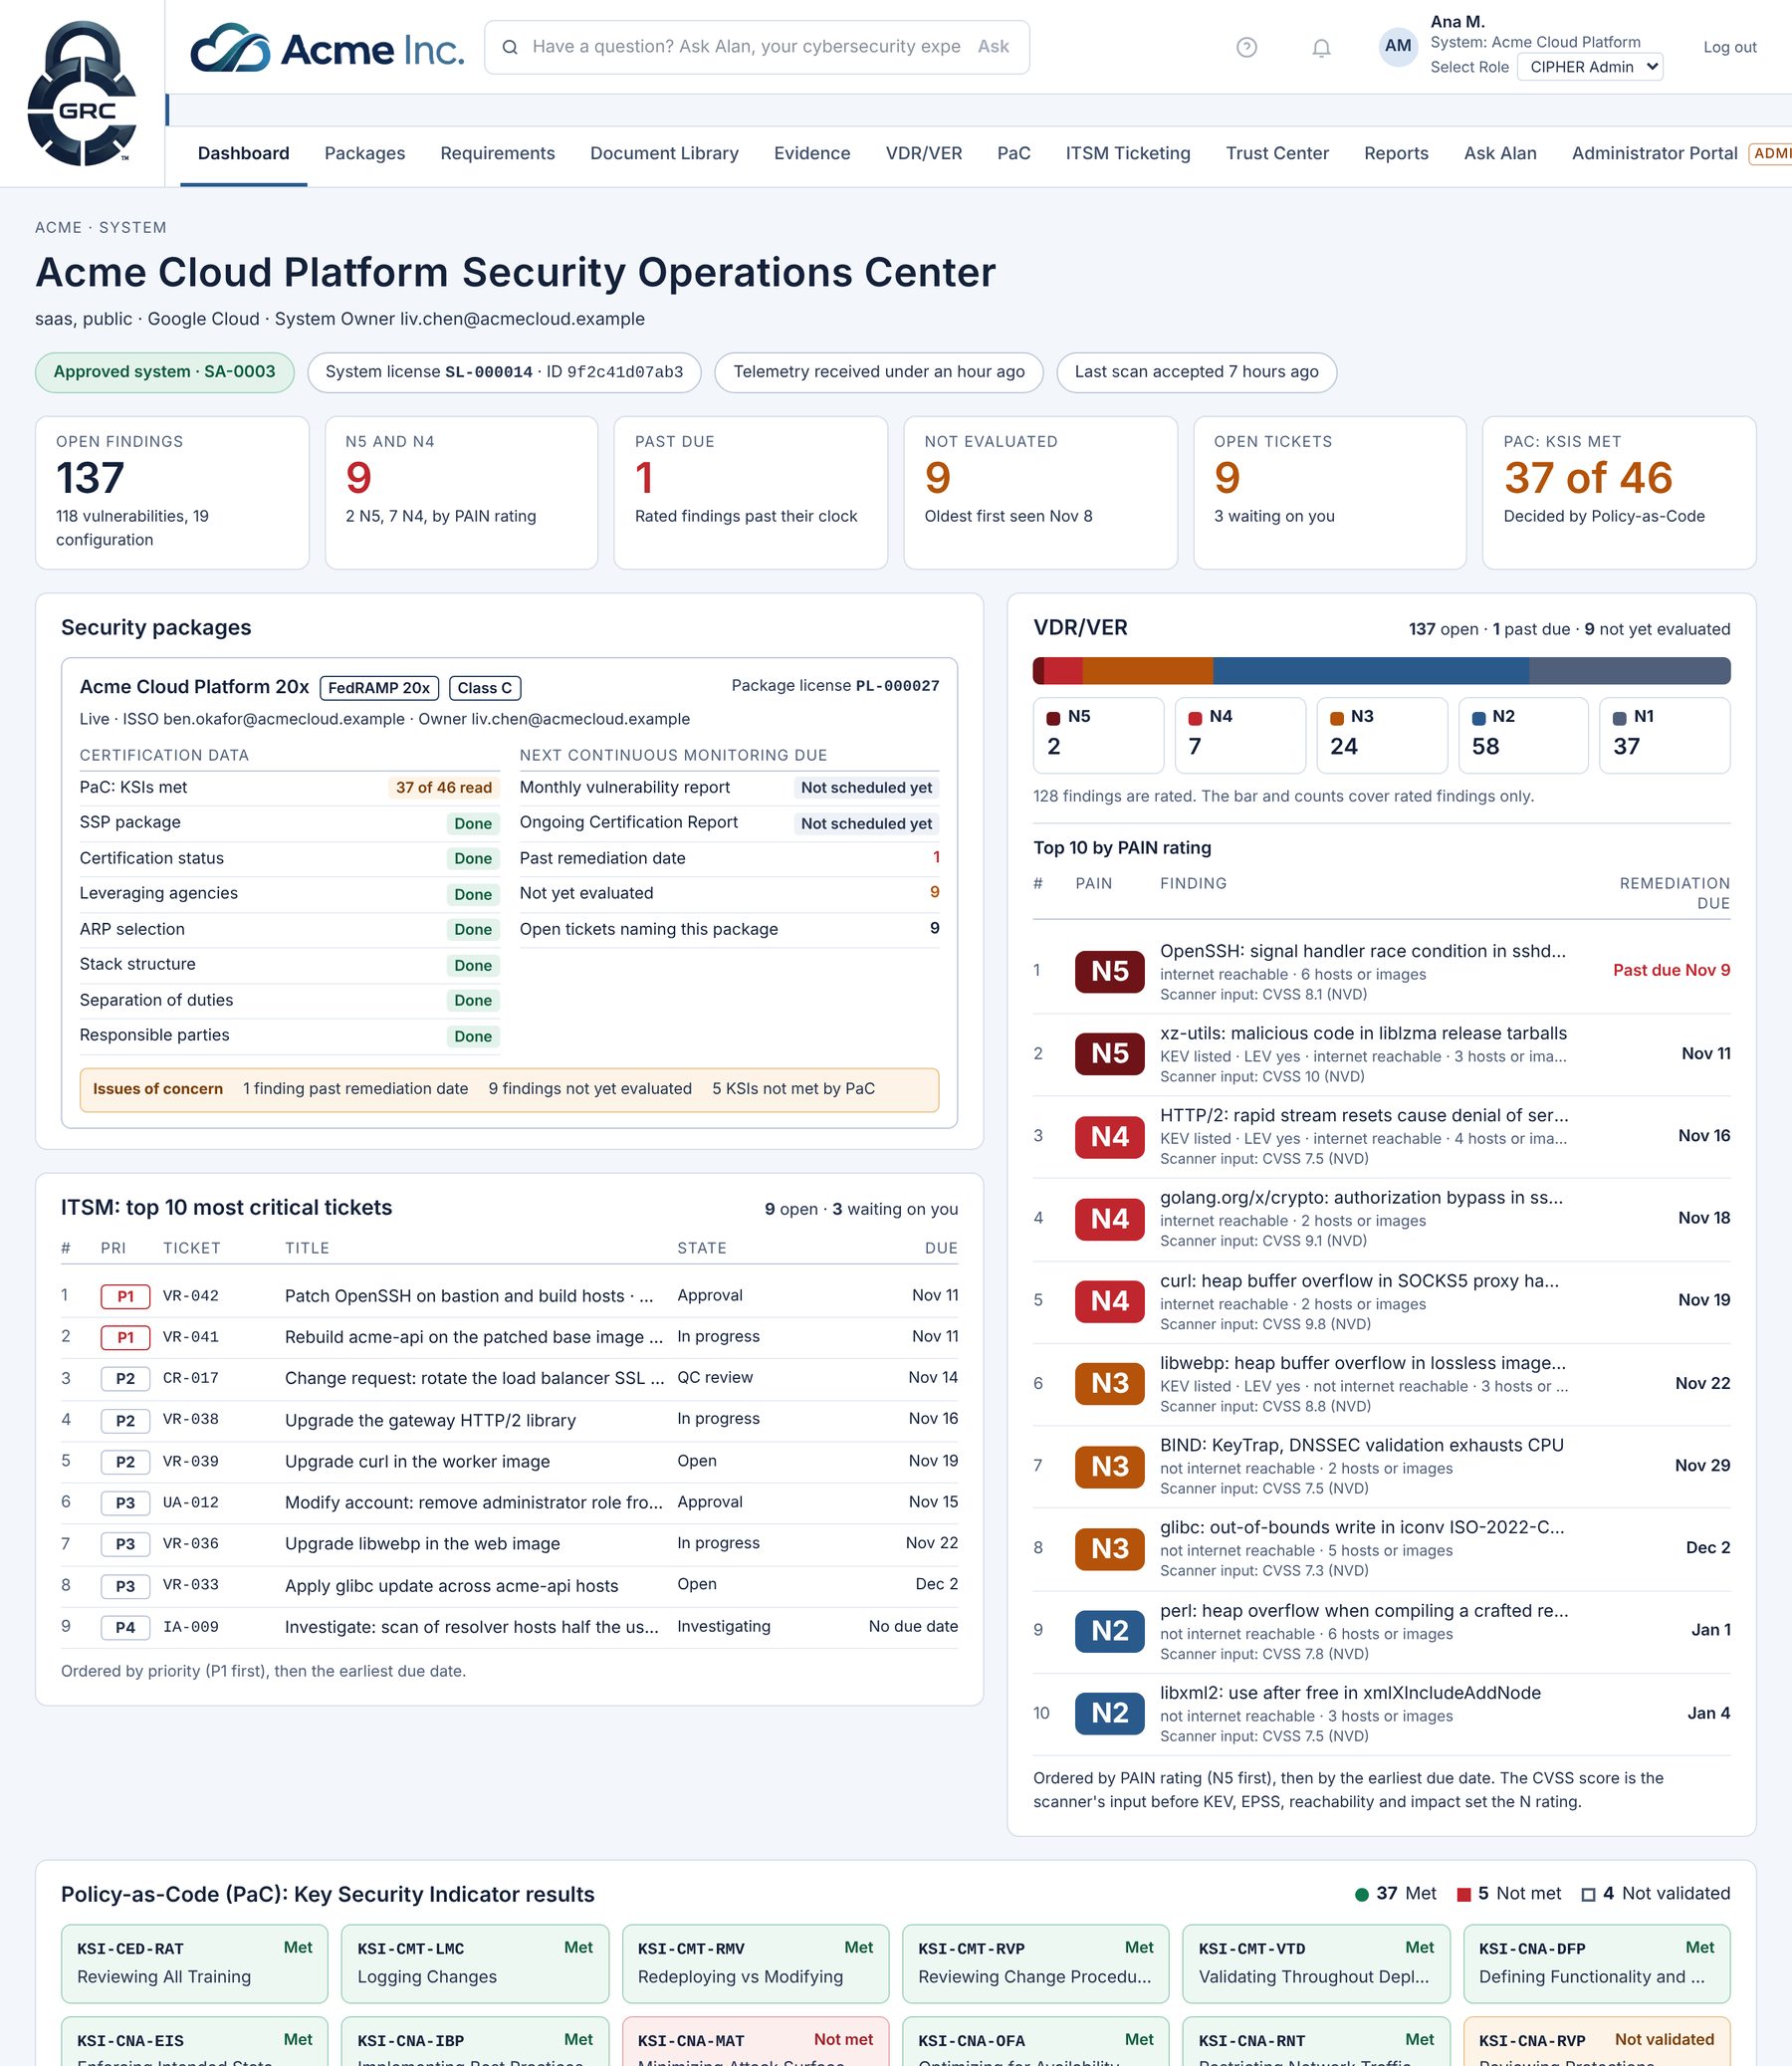
Your security operations center
Open findings by risk rating, the tickets waiting on you, and all 46 Key Security Indicators, updated from live telemetry.
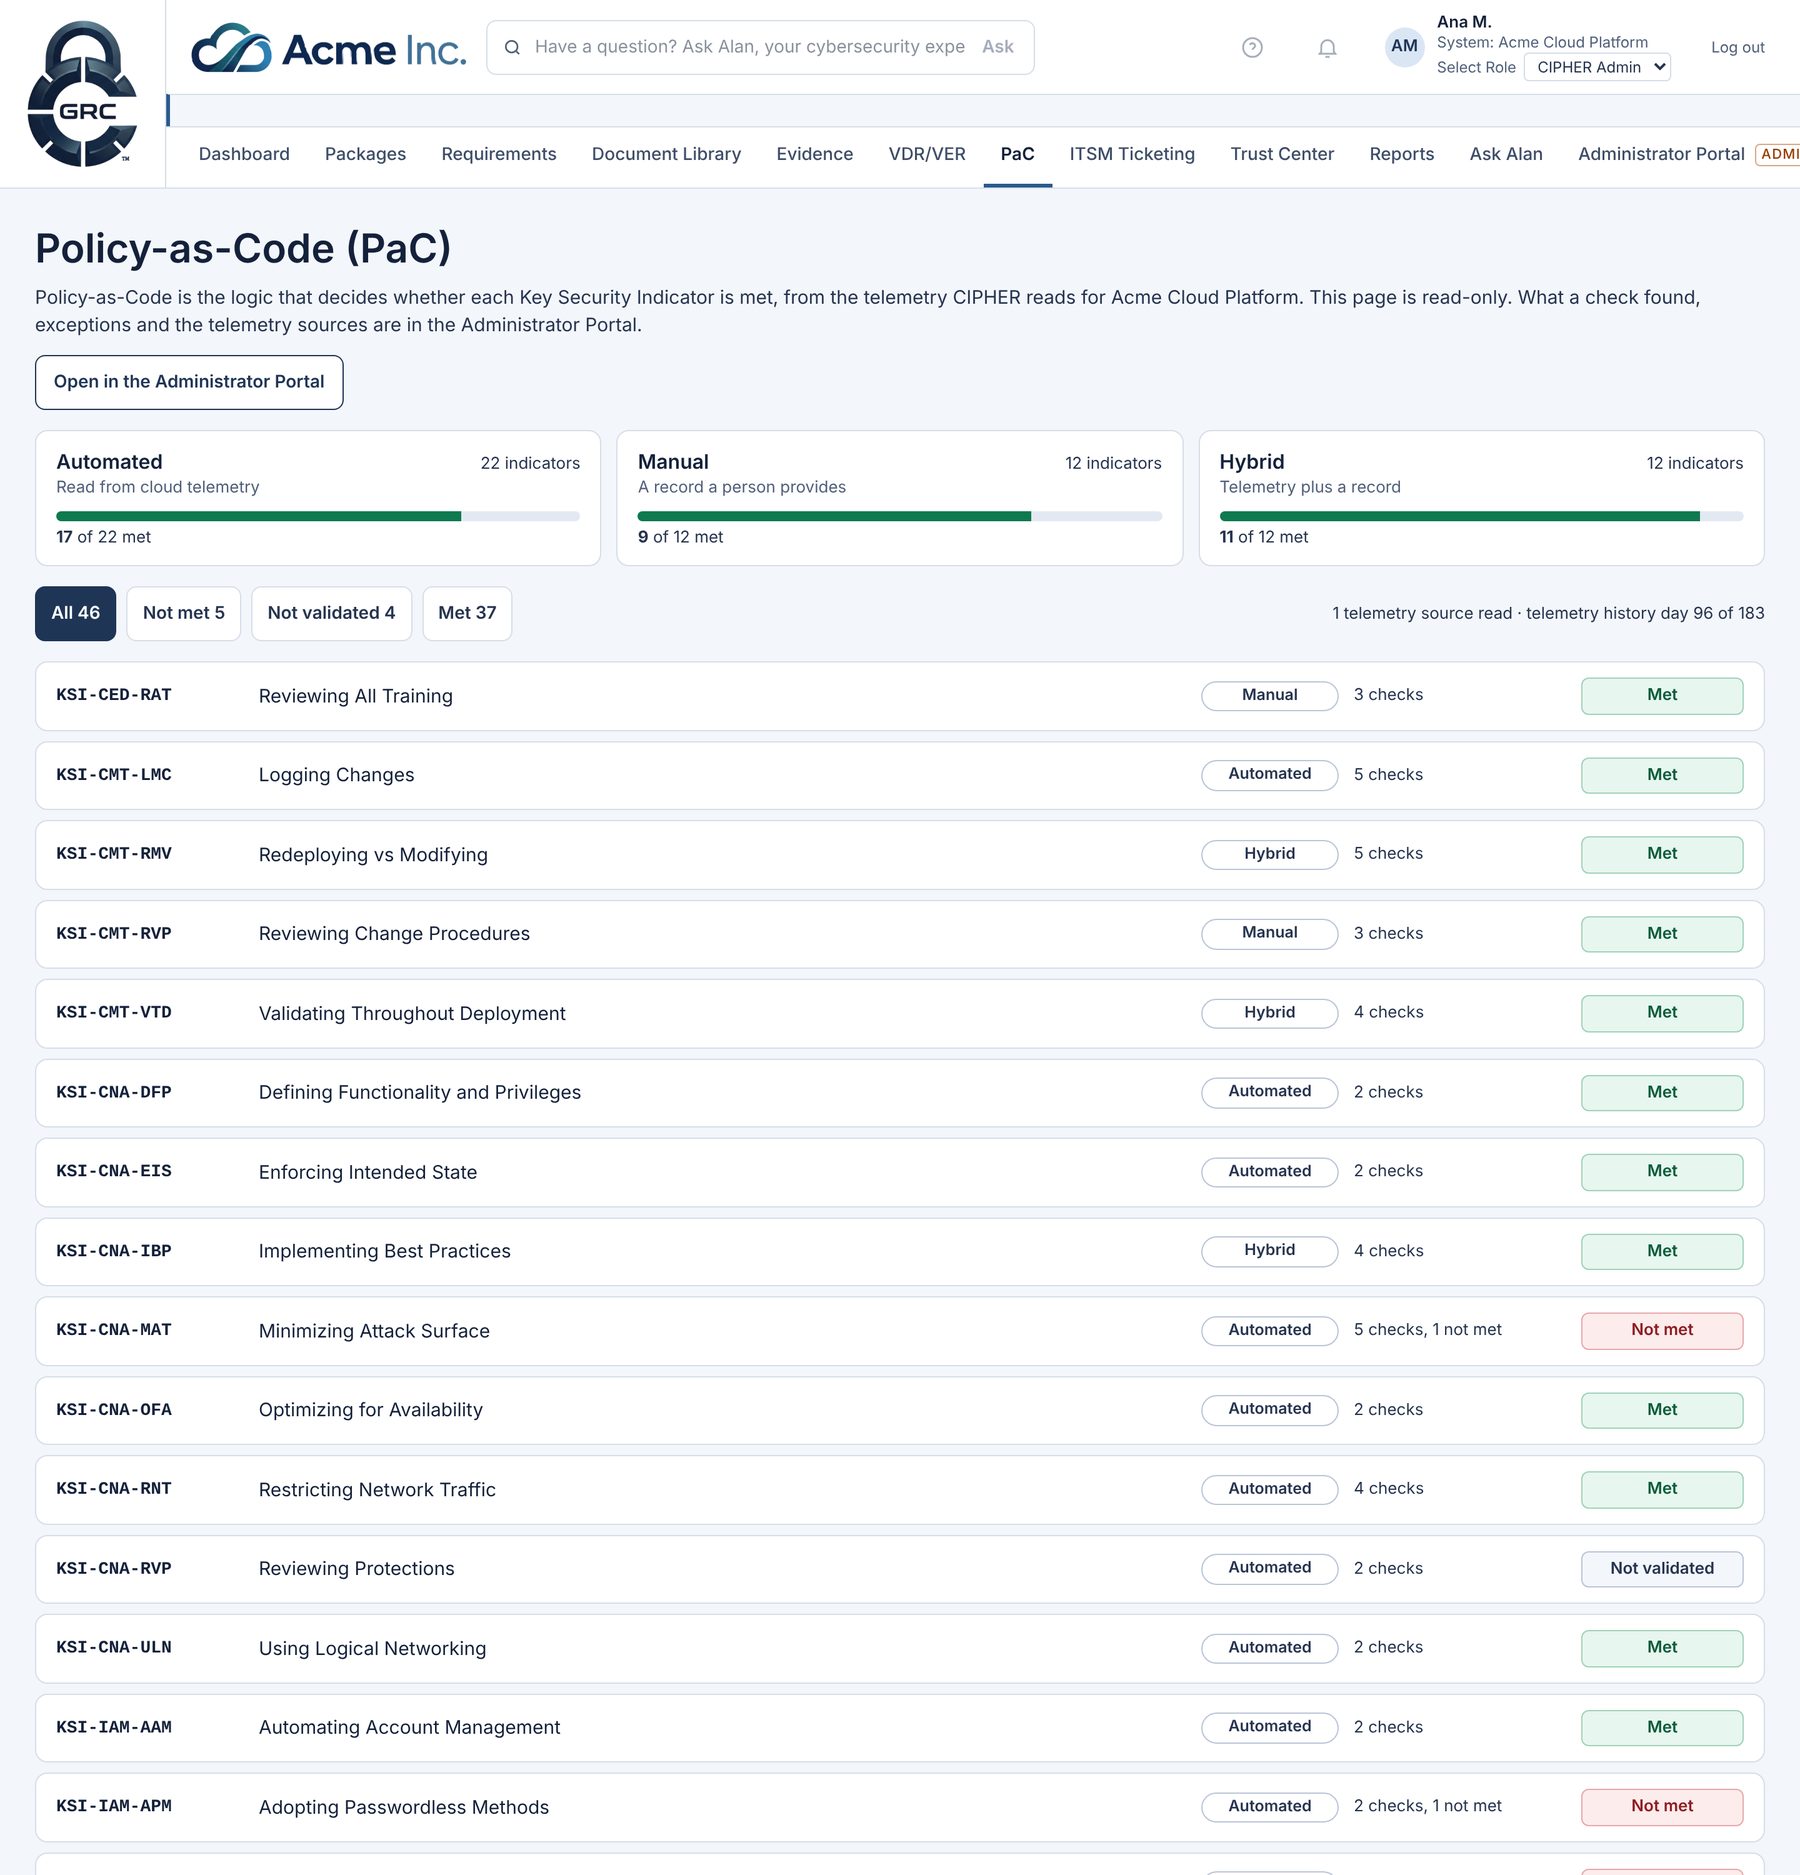
All 46 Key Security Indicators, decided by policy-as-code
Automated indicators are read from your cloud. Manual and hybrid indicators carry the record a person provides. Fixed rules decide every result.
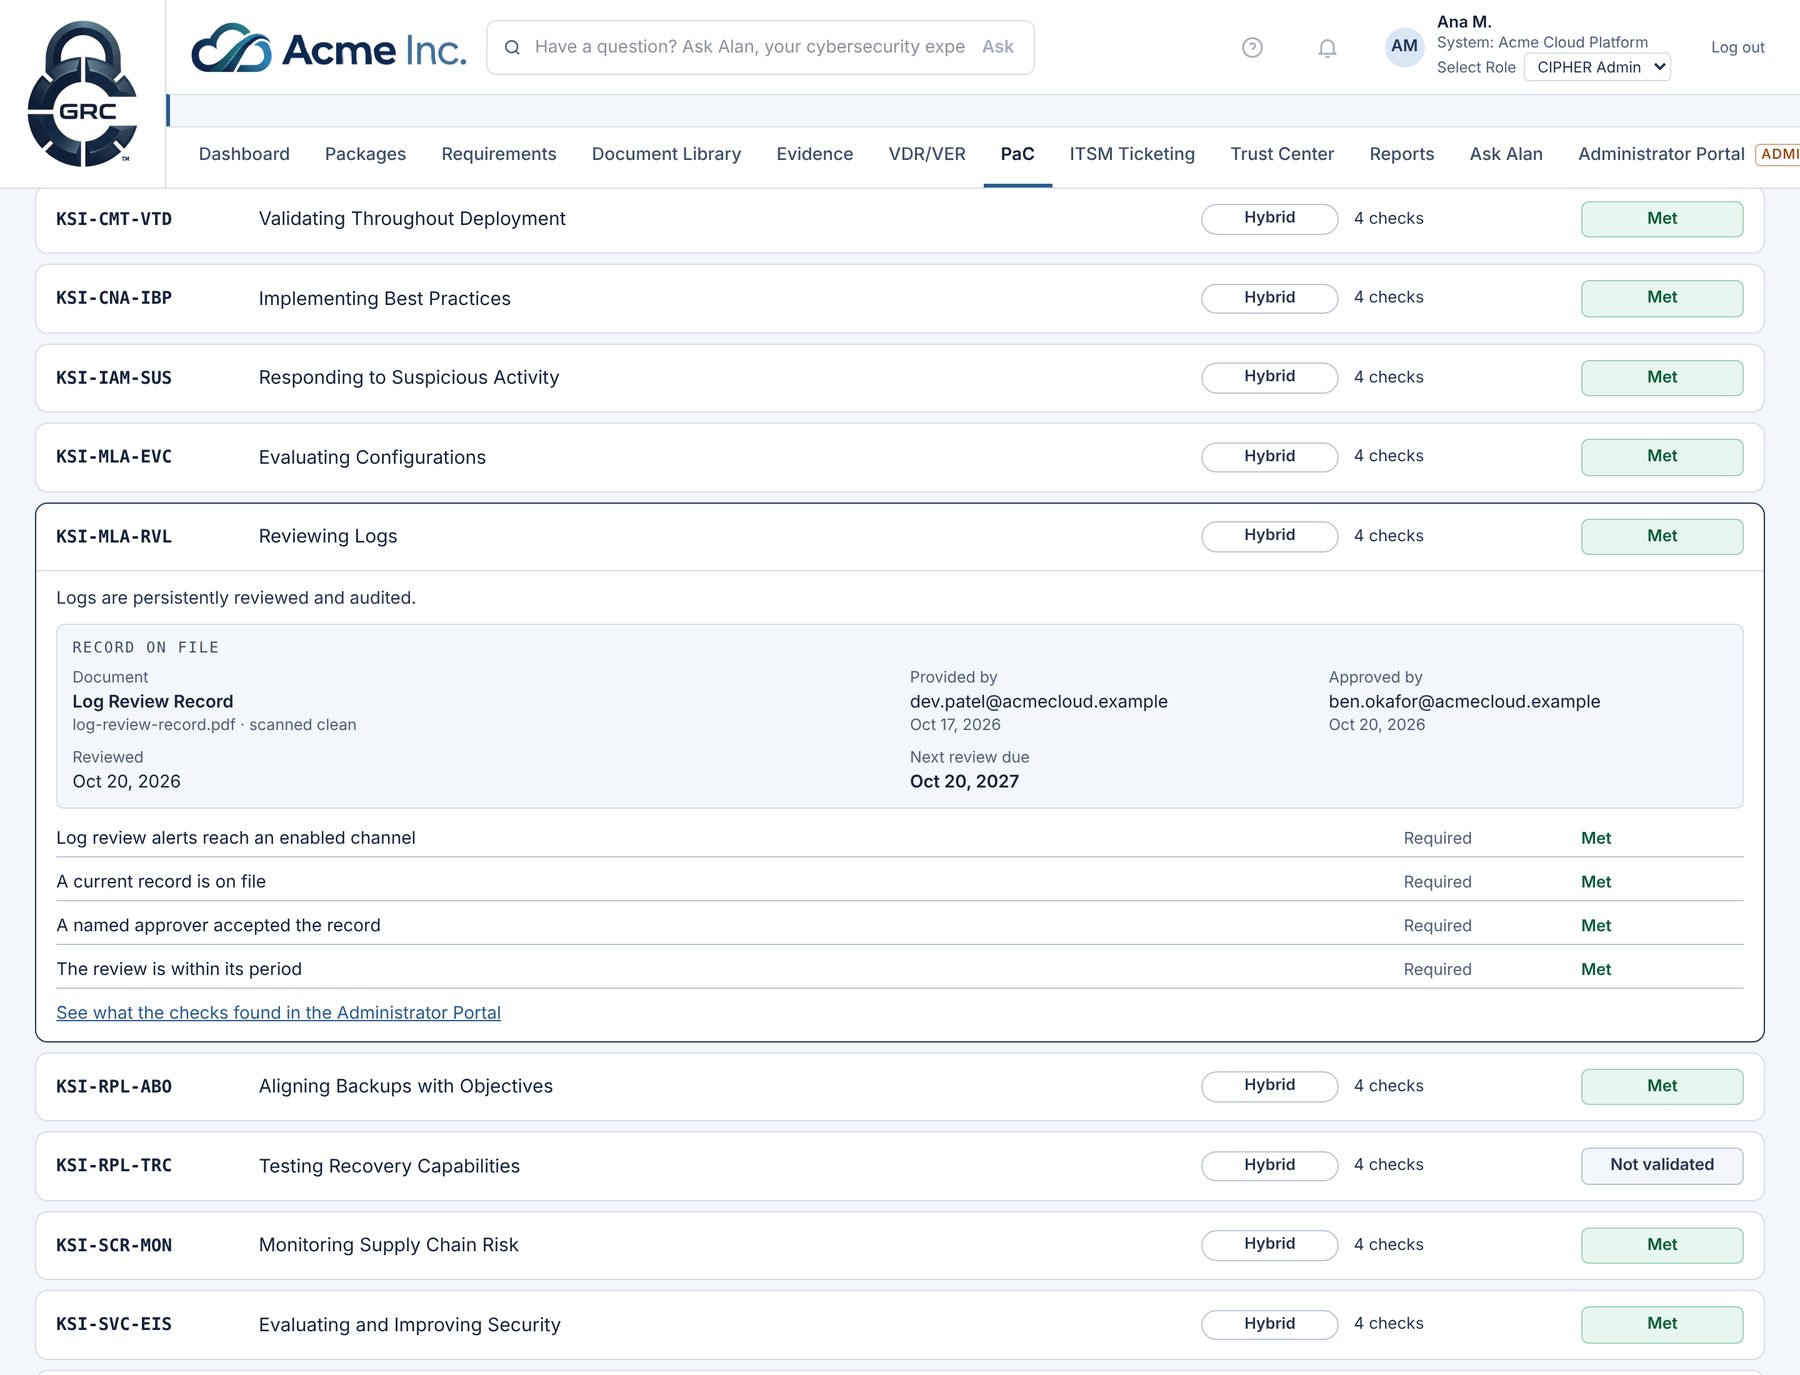
Every indicator shows its proof
The checks behind the result, the record on file, who provided it, who approved it, and when the next review is due.
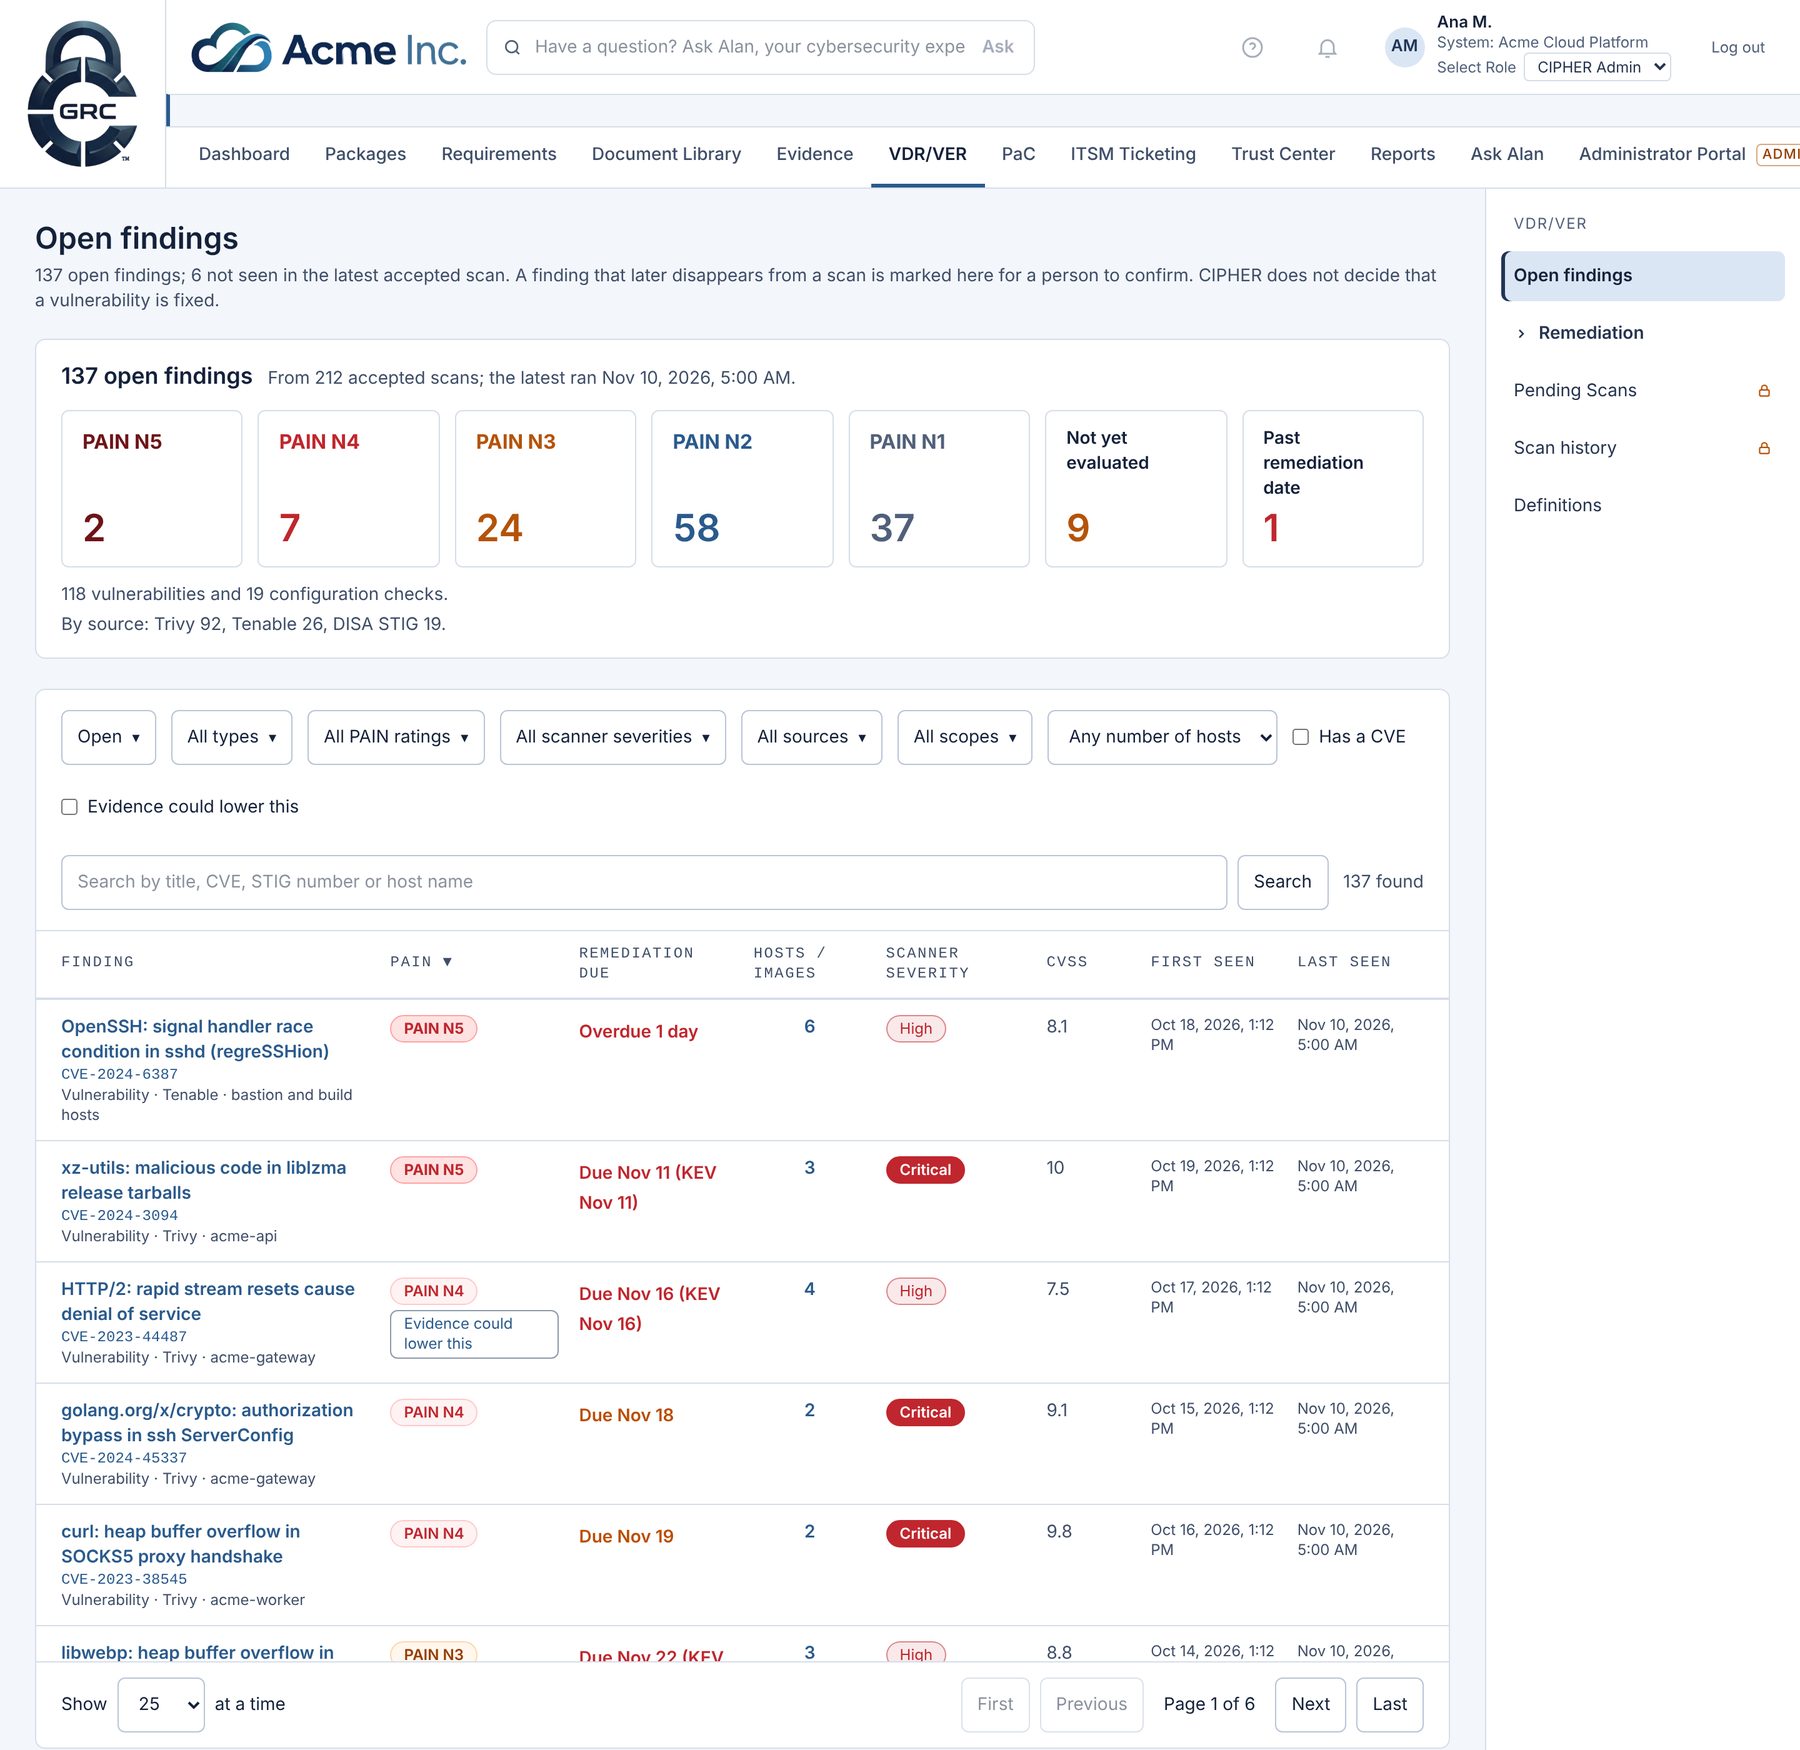
Vulnerabilities ranked by real risk
Findings from the scanners you already run, ordered by PAIN rating and tied to the remediation clock. The scanner score is an input, not the answer.
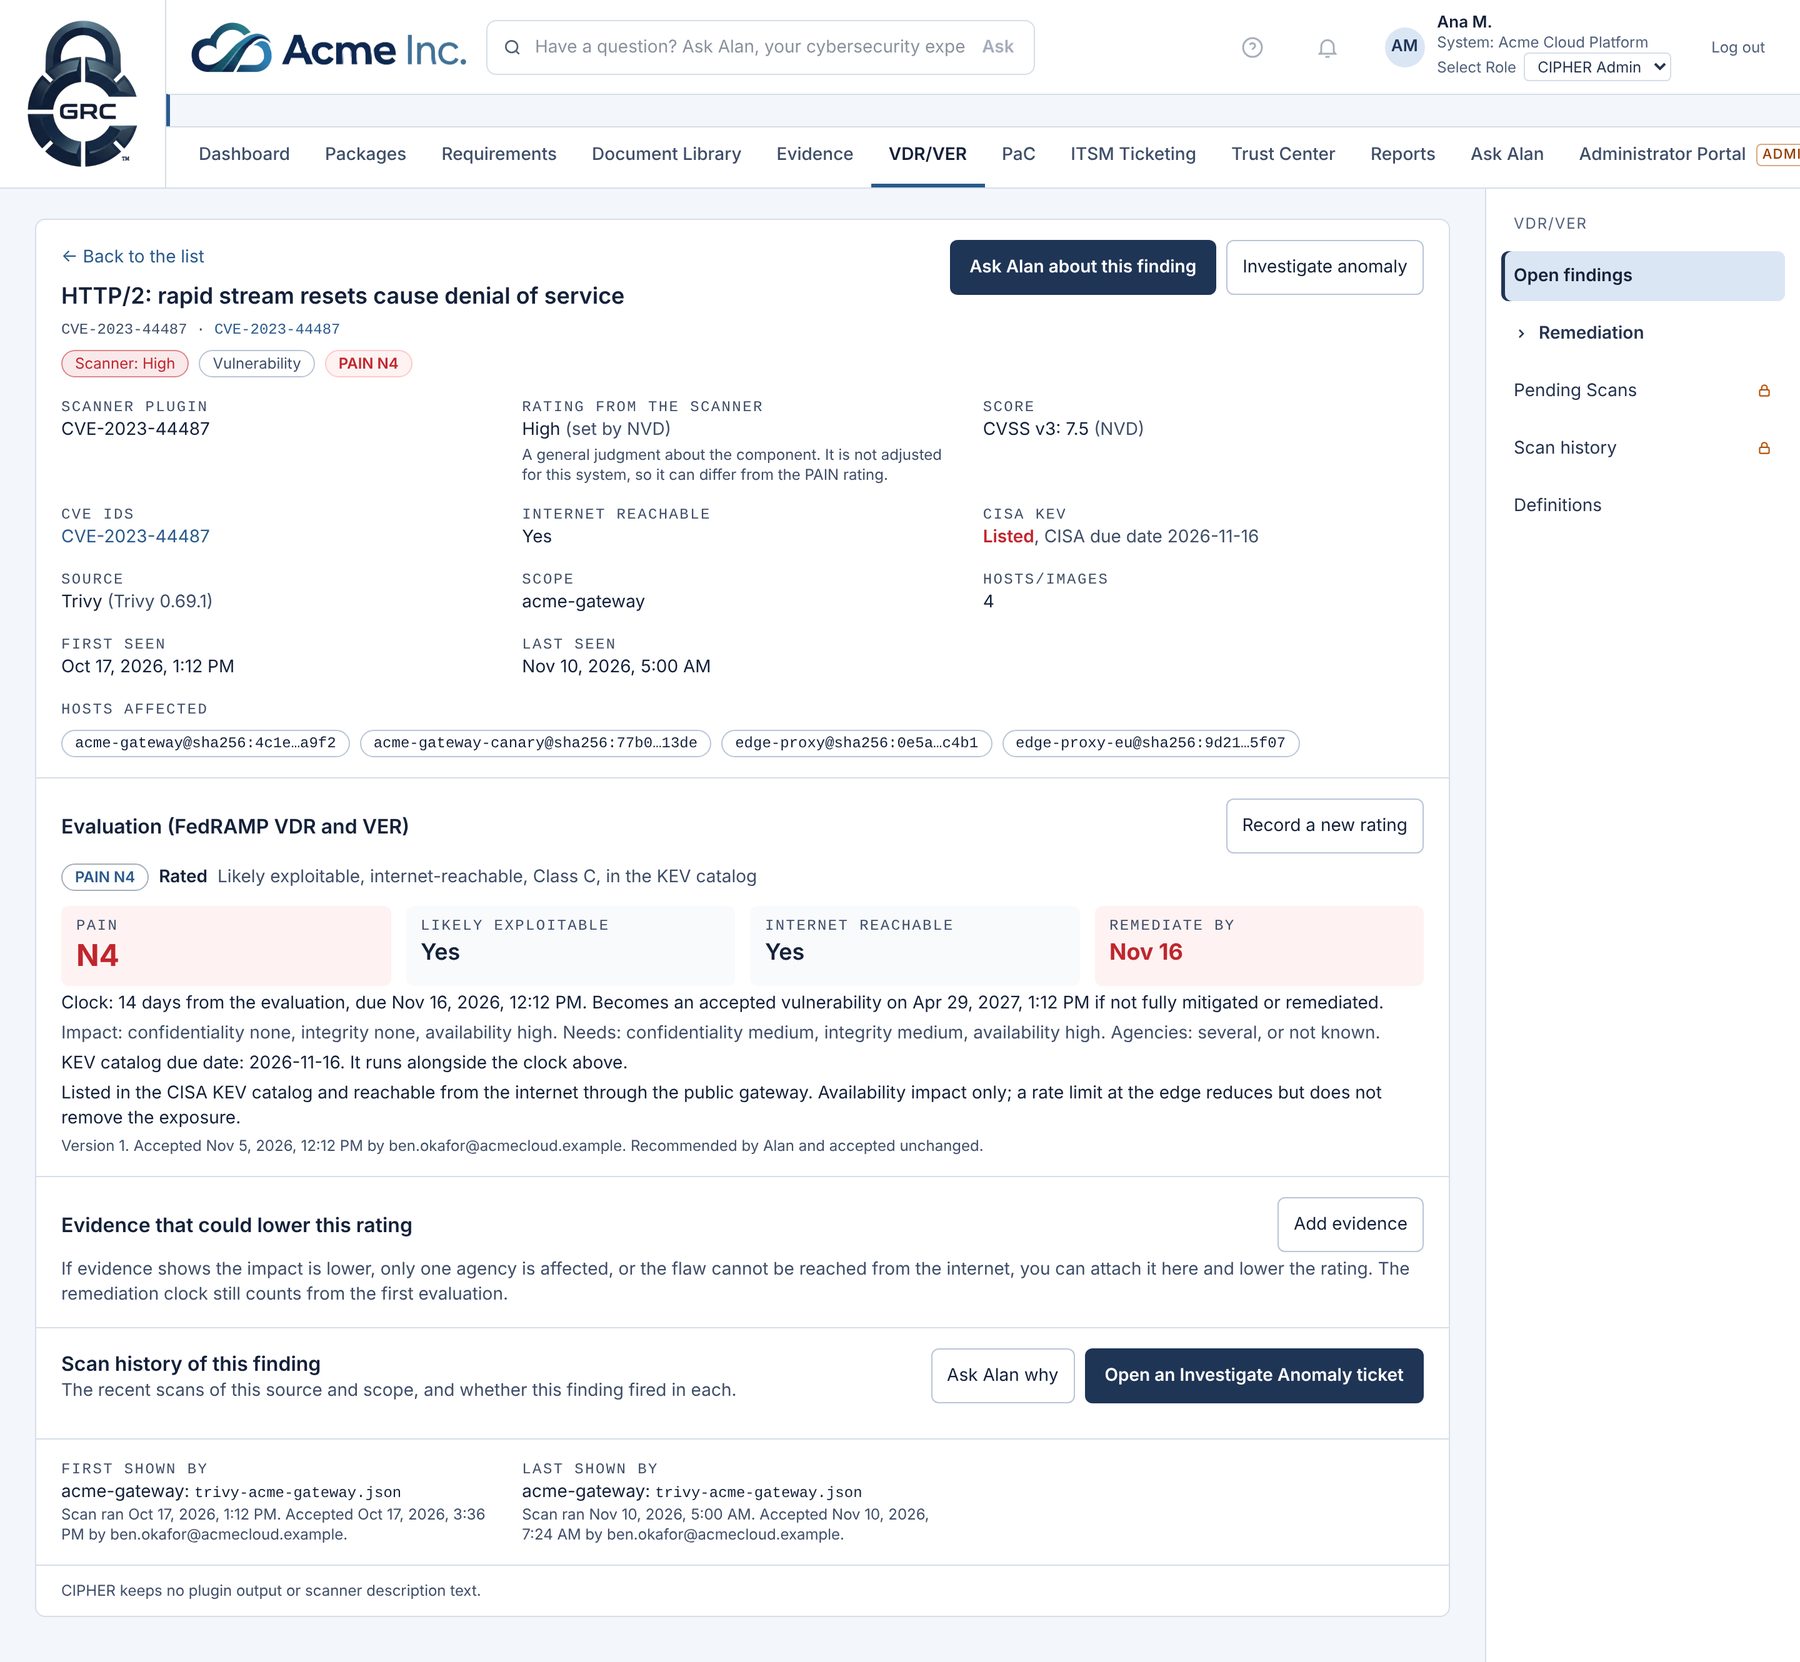
One finding, start to finish
Where it was seen, whether it is in the CISA KEV catalog, the rating and its reasons, and the date it must be remediated by.
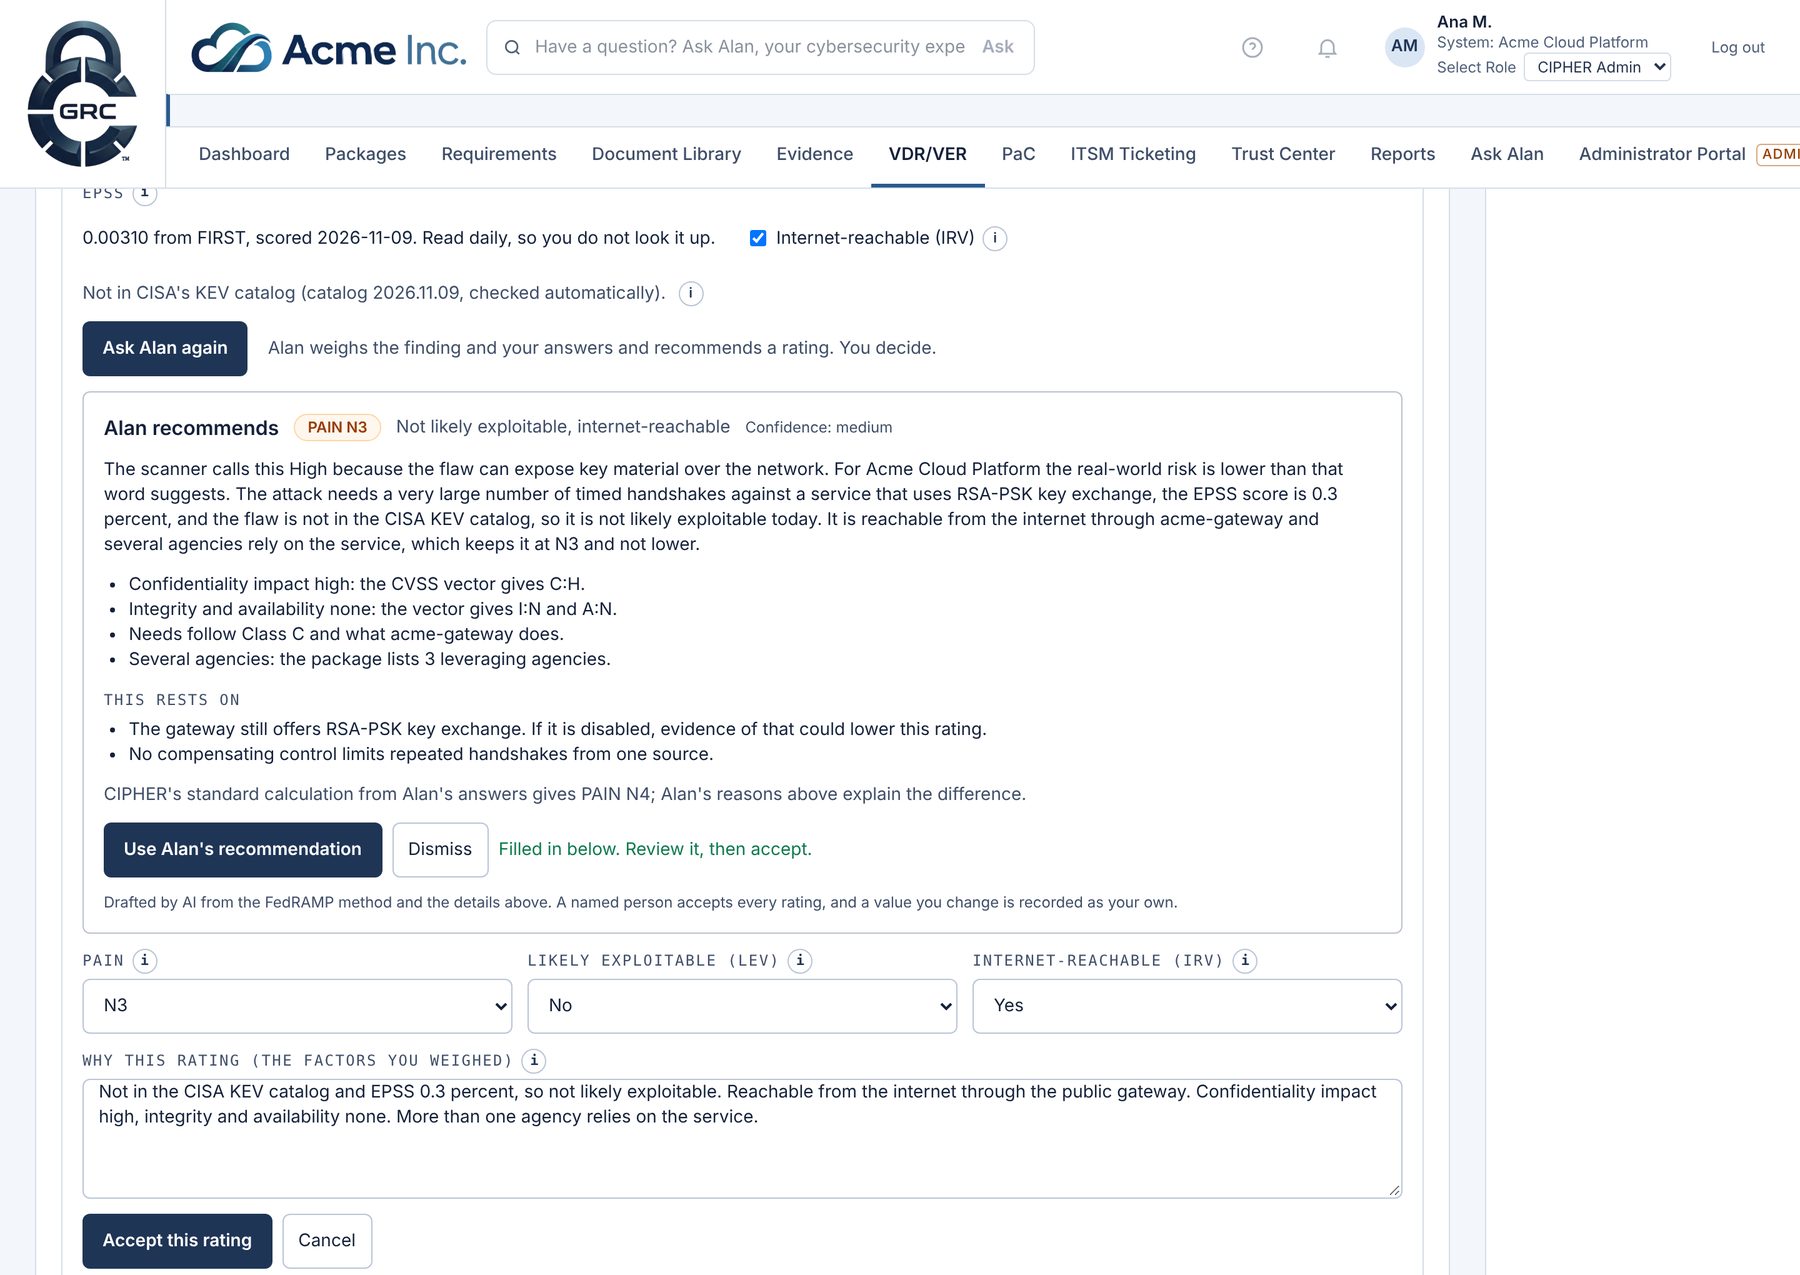
Alan recommends the rating and shows his reasoning
Alan weighs exploitability, reachability and impact for your system and explains the result in plain words. You accept, revise, or decline.
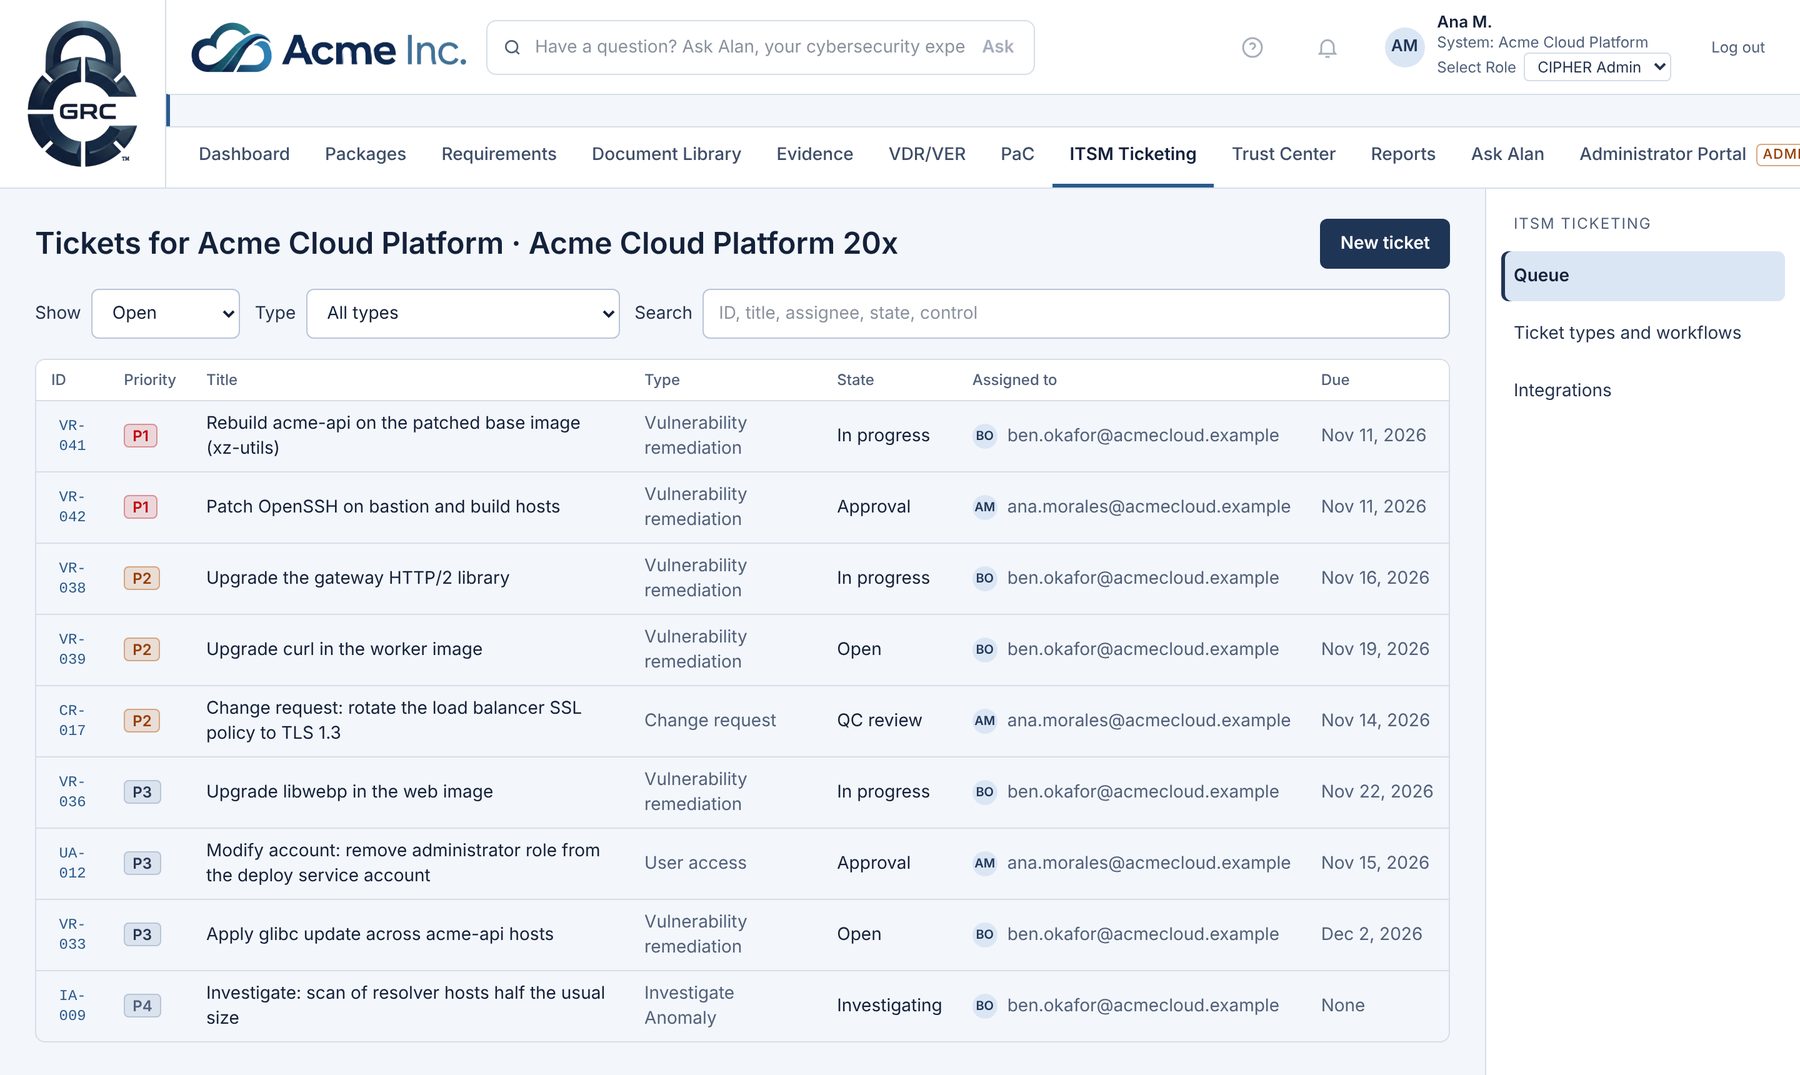
One queue, a full audit trail
Vulnerability work, changes, access requests and approvals together, each with its audit trail.
Ask in plain words, get an answer with its source
Alan answers from FedRAMP's published rules and your own records, names the rule behind each answer, and leaves the decision to you.
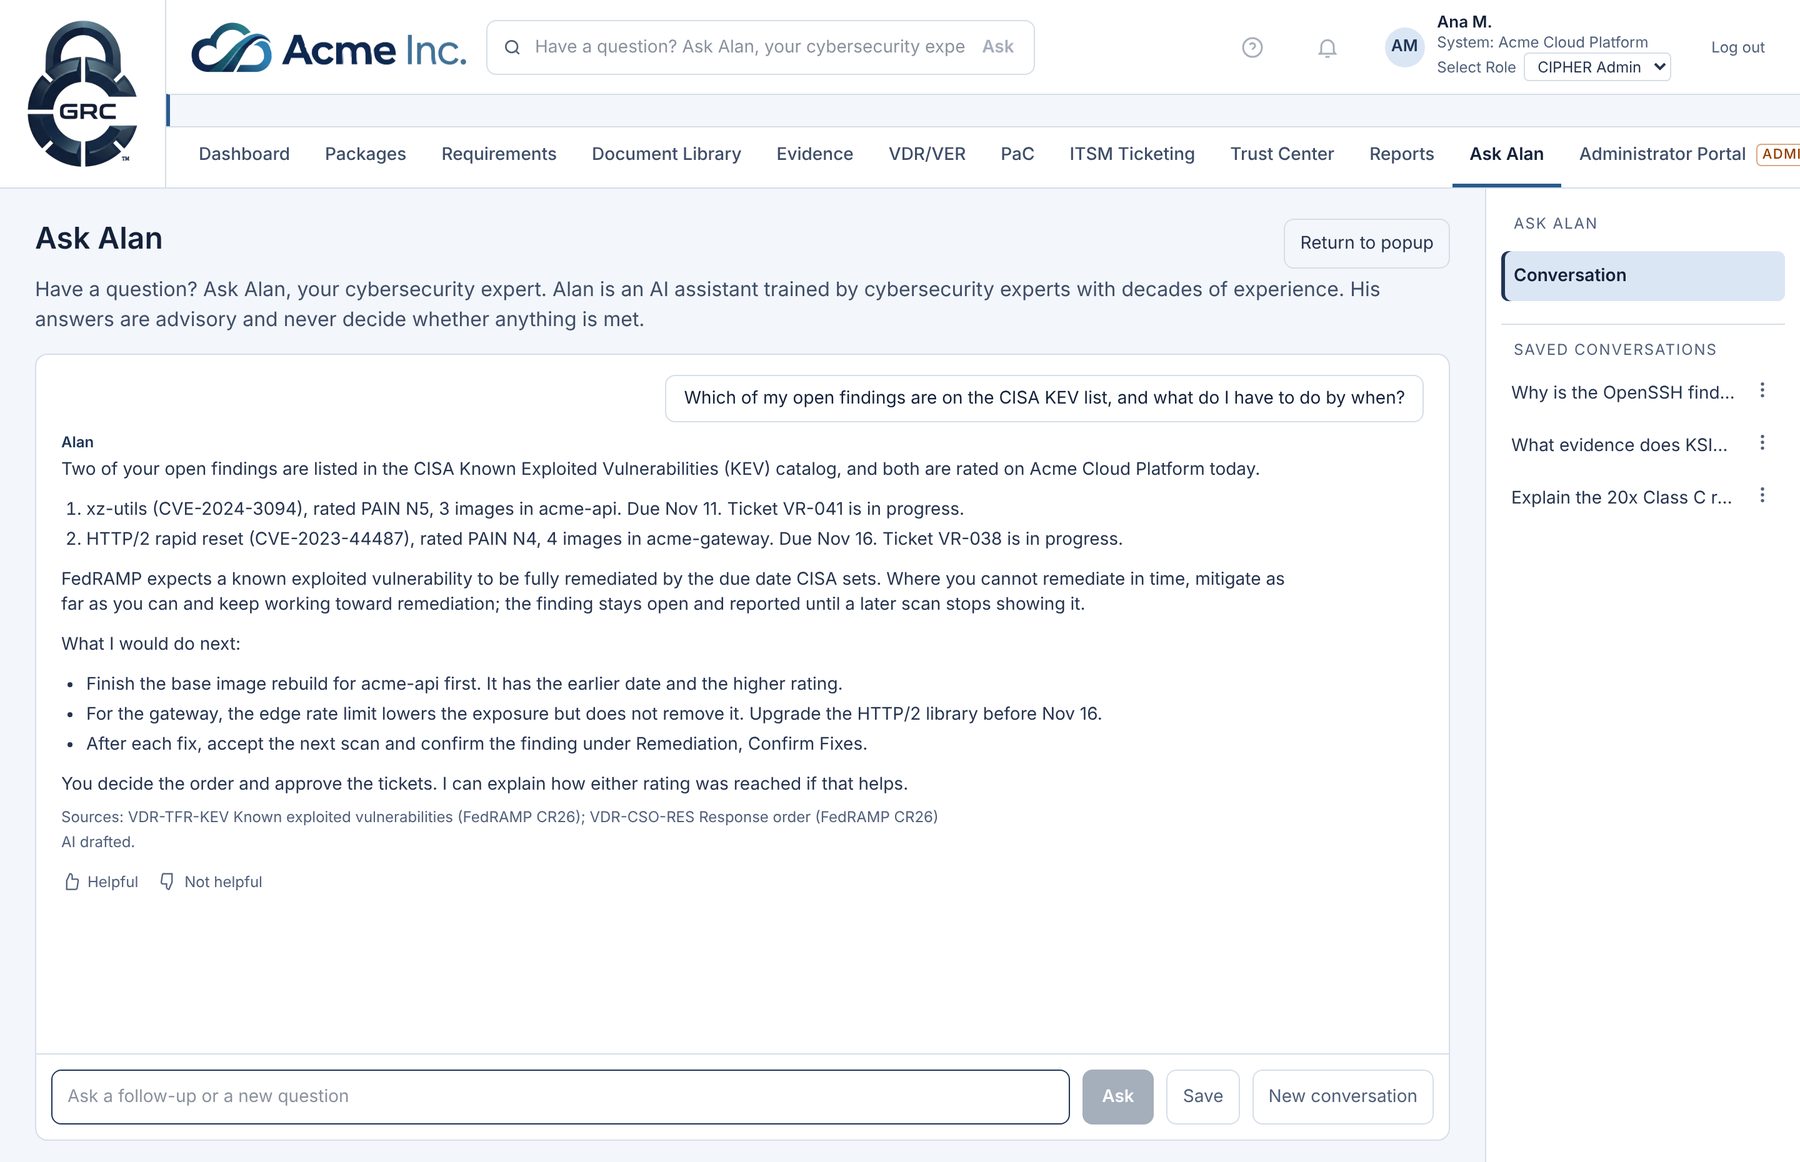
One trust center for the public and every agency
What you share with the public and with each agency, prepared from the same records your team works in. Updates are staged first and nothing is published until it is approved.
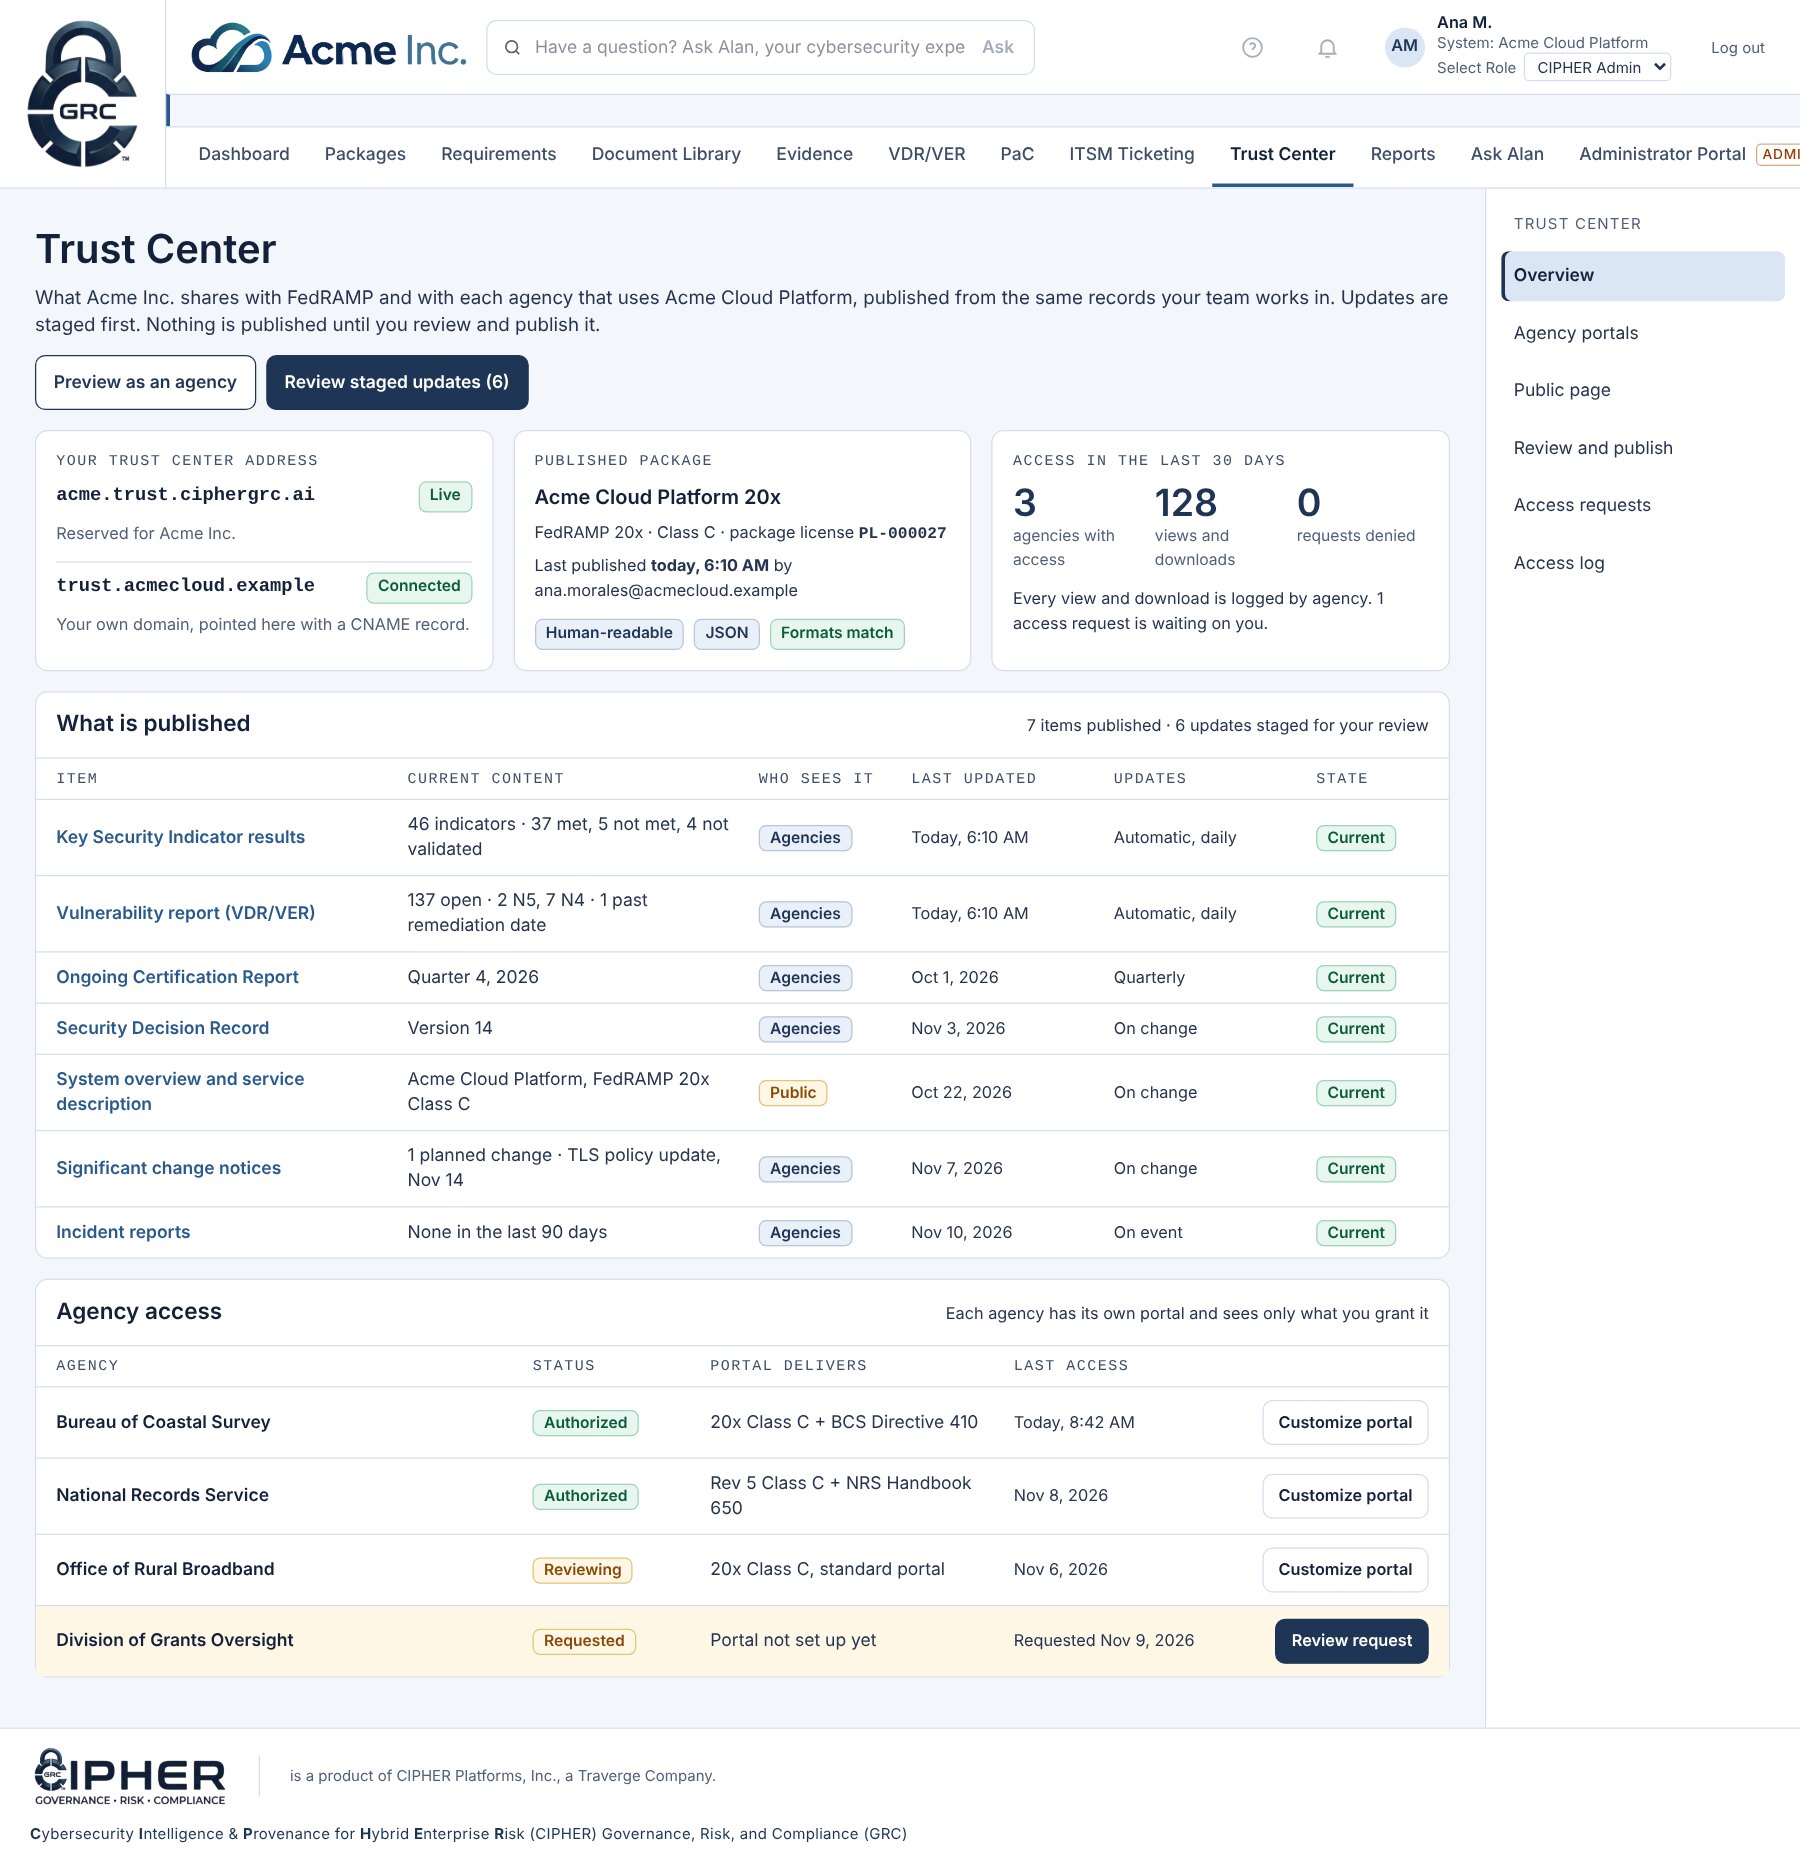
A portal for each agency
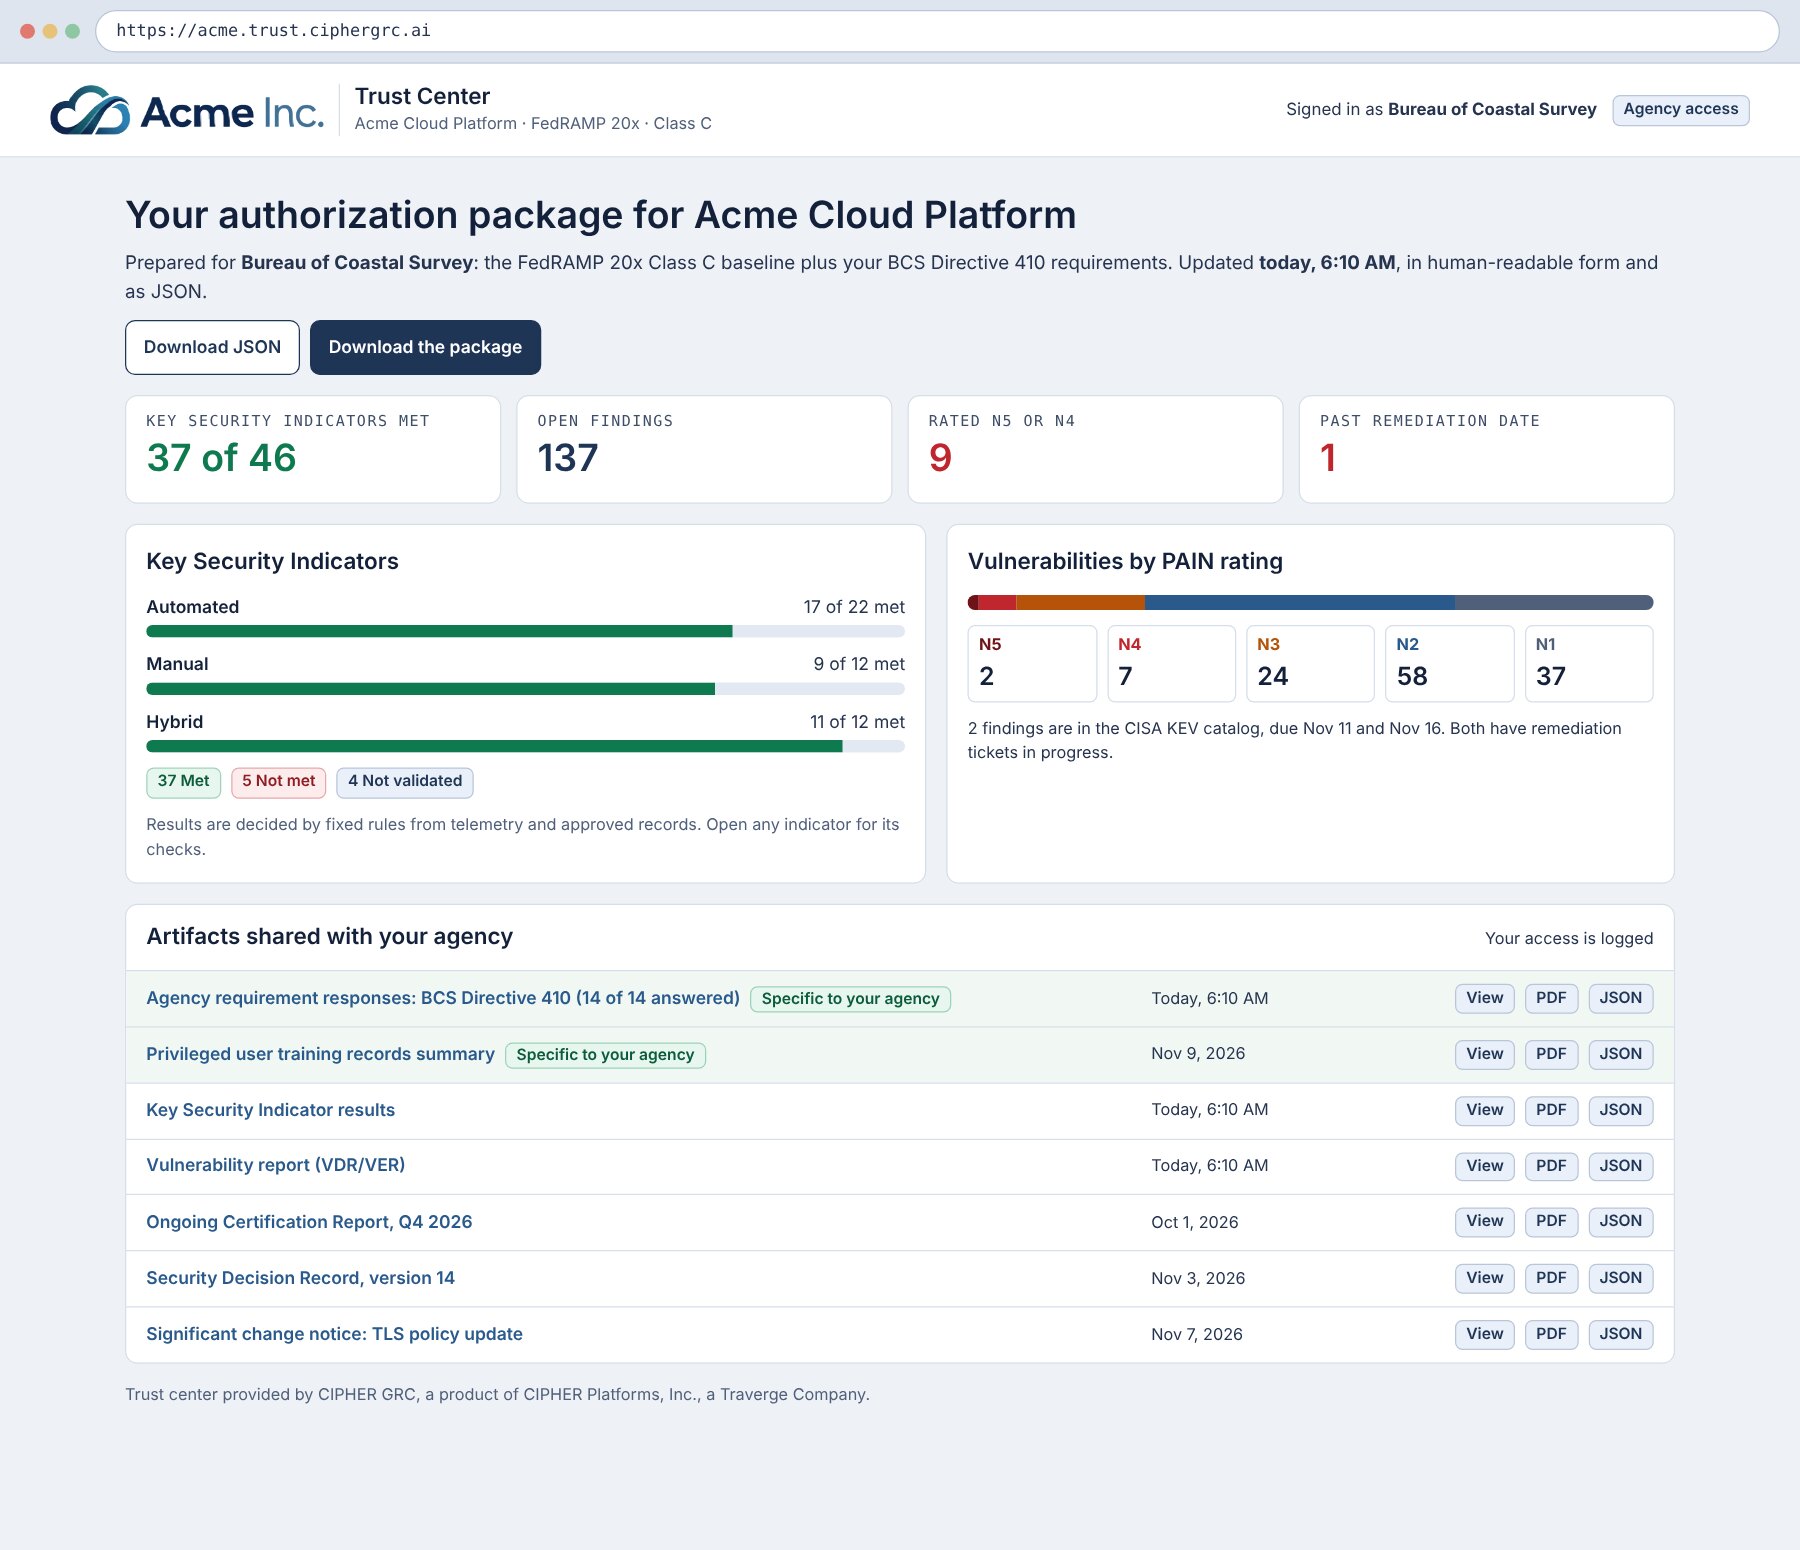
Each agency gets its own portal with the package it authorizes and the requirements it adds, in human-readable form and as JSON.
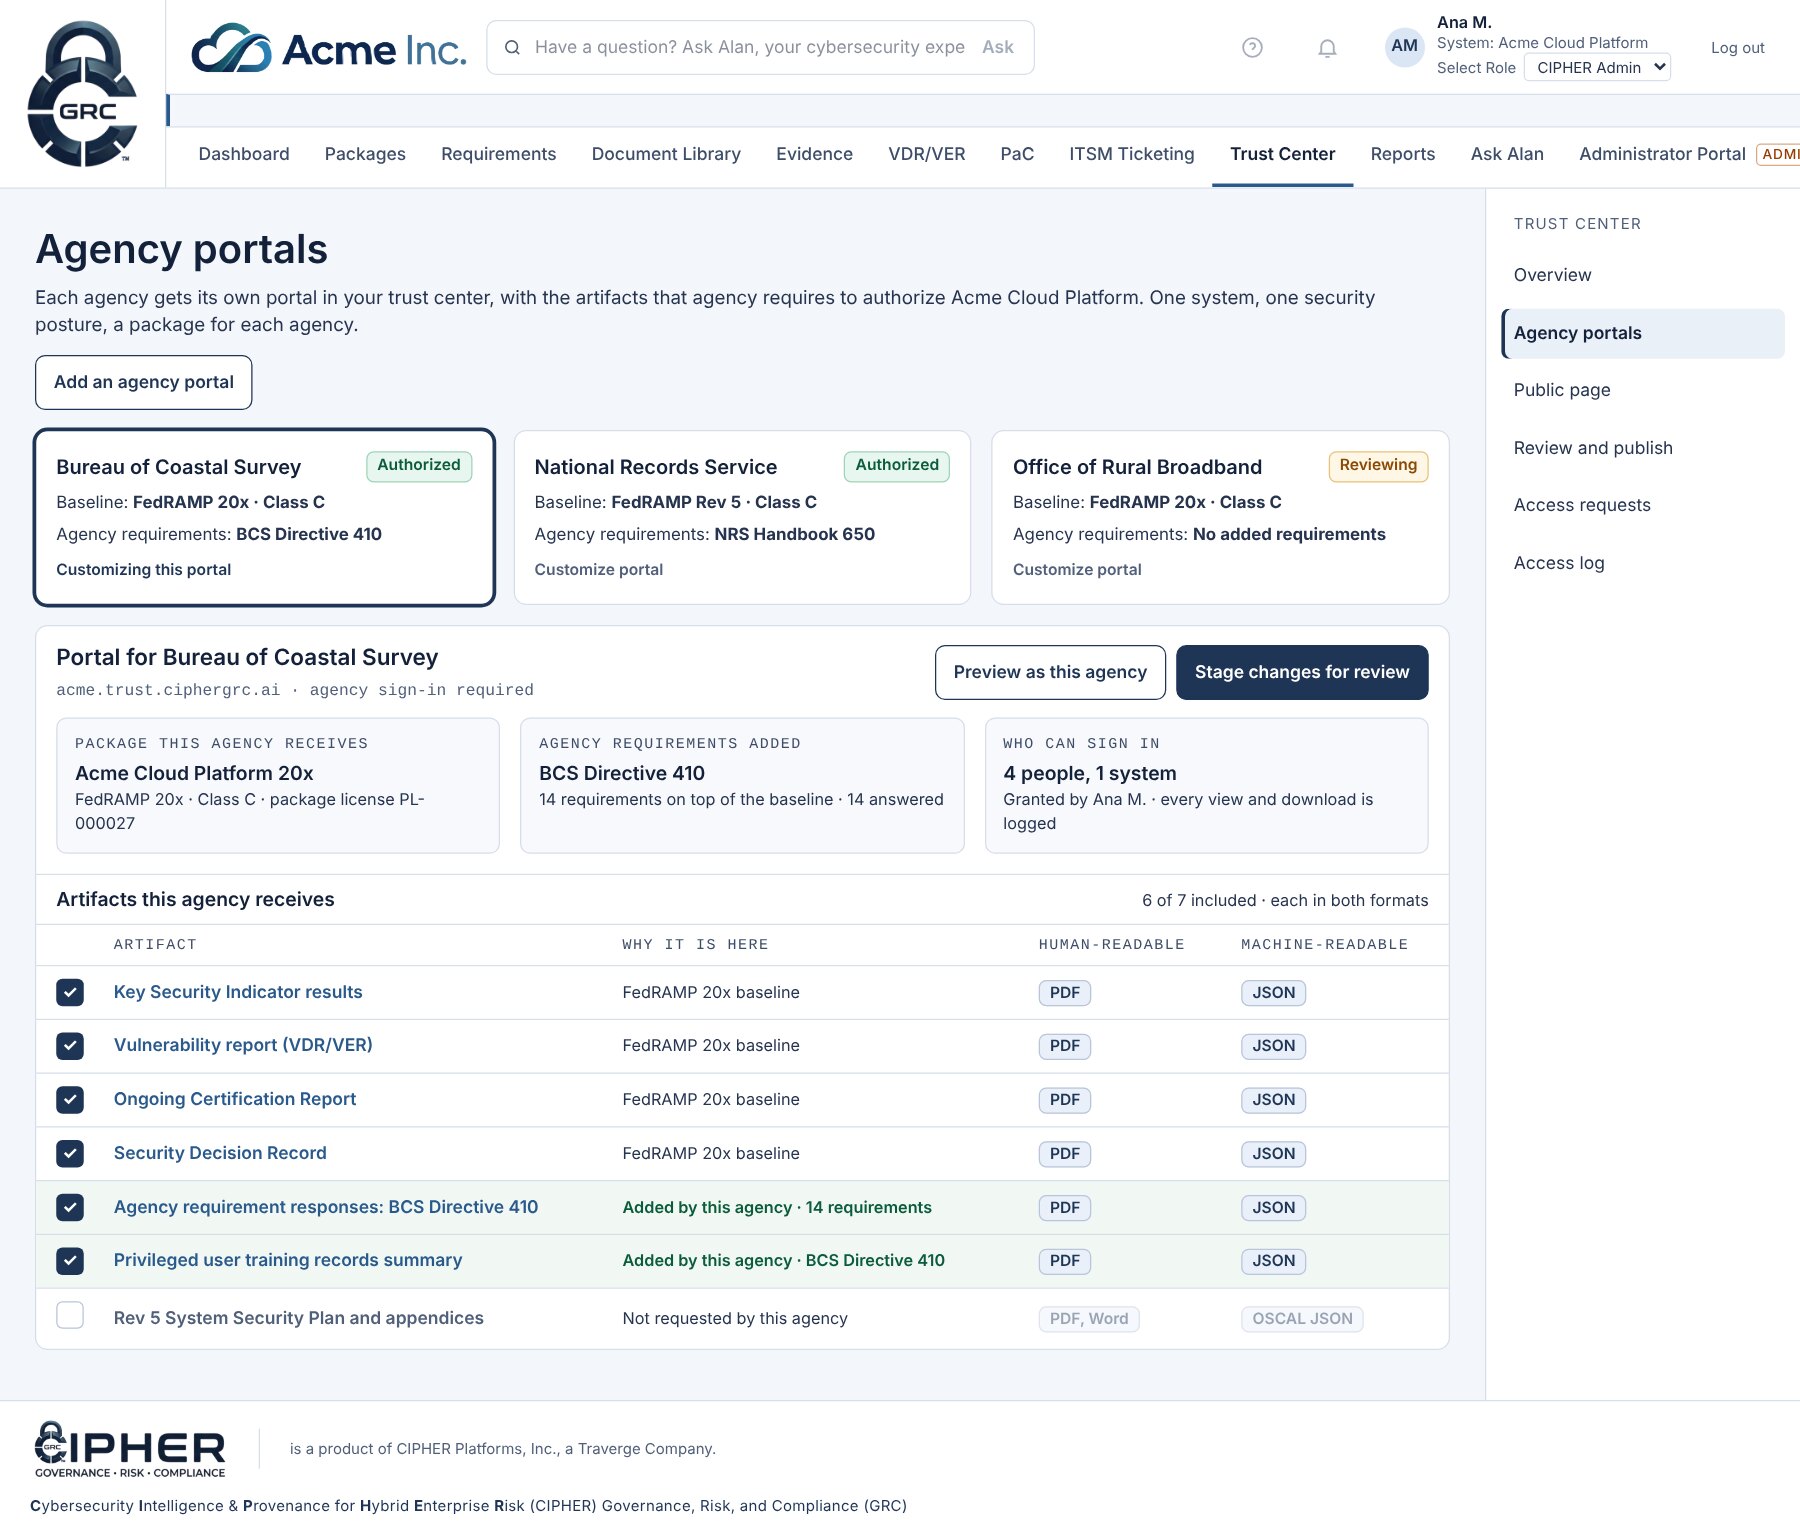
Review every update before it is published
Staged updates show what changed and who will see it. A named person gives the final approval, and an agency-specific update stays inside that agency's portal.
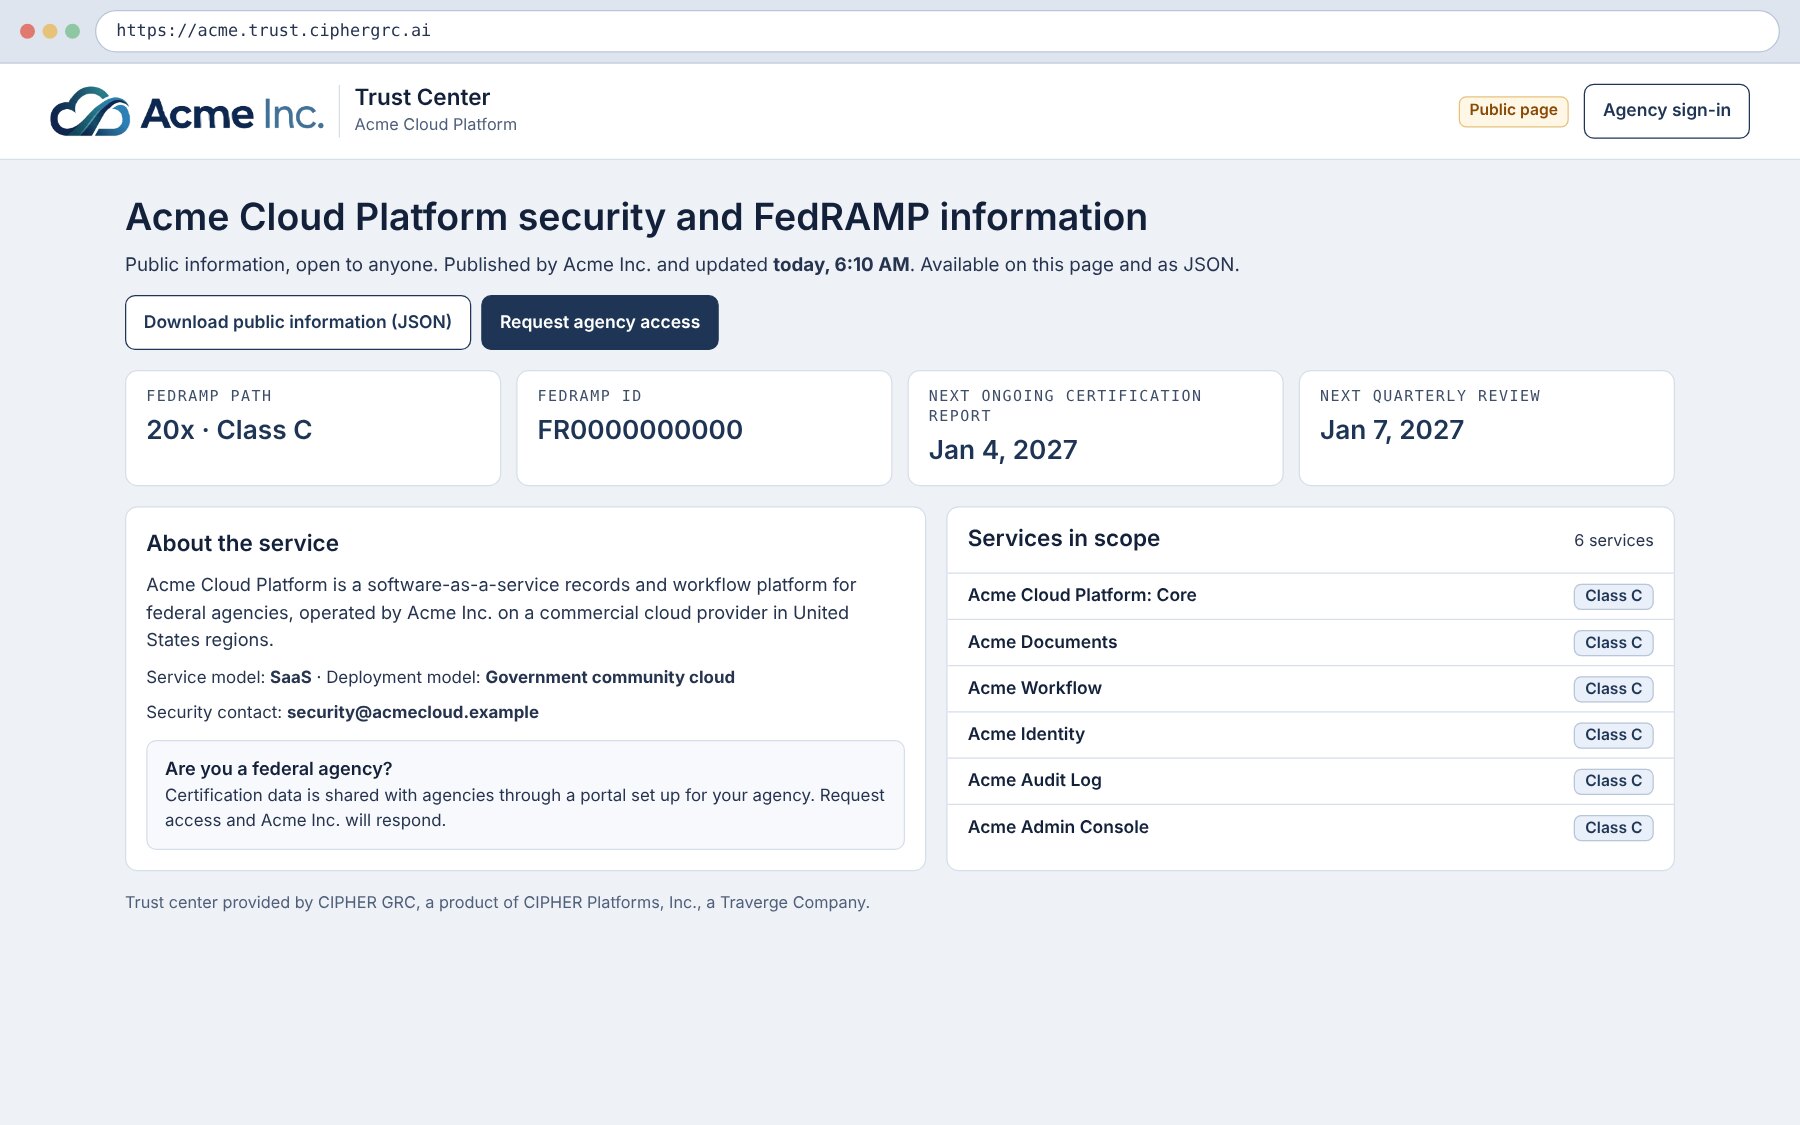
What anyone can see
Your public page carries the information FedRAMP expects every provider to share openly, as a page and as JSON.
What your agencies see
Current indicator results, vulnerabilities by risk rating and the artifacts specific to that agency, with every view and download logged.
Scroll inside a screen to see the rest of the page.
Is your program ready for CR26?
FedRAMP's Consolidated Rules for 2026 change how every provider proves its security, whether you are new or already authorized.
Every program starts on FedRAMP 20x
We onboard every customer on the 20x track. It is the fastest way to meet the vulnerability rules due on 7 December 2026 and the rest of the immediate CR26 requirements.
Build your program on 20x from day one
Stand up a Class C program built on Key Security Indicators, measured from your running cloud environment.
- Guided onboarding of your system, led by Alan AI and confirmed by you
- Read-only telemetry from your cloud accounts, on any major cloud
- Indicator results decided by deterministic rules, never by a model
Meet the CR26 deadlines now, on 20x
Keep the authorization you earned. We onboard your system on the 20x track first, so vulnerability detection, evaluation and reporting are in place by the deadline.
- Scan results from the scanners you already run, in the formats they produce
- Every finding evaluated and tracked to its remediation date
- Rev. 5 package support is in development and follows the 20x launch
One platform for the full FedRAMP workload
Providers shouldn't have to assemble a FedRAMP program from five tools and a consulting bench.
Federal compliance can read like a cipher. Alan helps you decipher it.
Much like the coded messages of the Enigma machine, federal compliance rules can be hard to decipher. Alan is the AI built into every page of CIPHER GRC. Ask in plain words and get a plain answer, with the rule it came from.
What Alan does
- Answers compliance questions and cites the rule behind each answer
- Recommends a risk rating for a finding and explains why
- Maps your architecture and data flows from what your cloud shows
- Groups findings that a single fix would clear
- Reviews evidence and tells you what an assessor is likely to ask
What Alan never does
- Decide whether a requirement is met: fixed rules do that, the same way every time
- Approve, accept or submit anything
- Change a setting in your environment
- Guess: when the rules do not answer a question, Alan says so
How Alan works
- Retrieval-grounded answers (RAG): Alan reads FedRAMP's published rules and the CIPHER compliance matrix before he answers
- Specialist agents for specific jobs, each working from your own records
- Every proposal is checked by code before you see it
- You approve, revise, or decline
Where Alan runs
- Only on AI models approved for FedRAMP and DoD workloads, called from inside a Google Cloud Assured Workloads boundary
- Never on public AI services, and your data is not used to train models
- A conversation is kept only if you choose to save it, in your own dedicated instance, encrypted with managed keys
- Alan sees only what your role is allowed to see
Alan is the name of the AI assistant in CIPHER GRC. It is not intended to represent any specific person, and it is not affiliated with or endorsed by any individual, estate or organization.
Software and the people who know how to use it
CIPHER GRC is never sold as software alone. Every license comes with named Traverge experts.
The CIPHER GRC platform
Your systems, packages, evidence, findings and tickets in one place, with a full audit trail.
Alan AI
Your cybersecurity expert on every page. Alan answers from FedRAMP's published rules, explains your next step, and leaves the decision to you.
A dedicated Customer Success Analyst
A Traverge analyst with verifiable experience in your package type, as your main point of contact for the program.
A dedicated Customer Success Engineer
A Traverge engineer with verifiable experience running the technologies your service is built on.
What changes for your team
Focus on your product
Your team builds and sells your cloud service, focusing its cycles on what matters most: your product and your reputation. CIPHER GRC and the Traverge team keep your service operating in compliance with federal cloud standards.
Reports for each agency
Give each agency that uses your service the view it needs, built from the same evidence. Rev. 5 package support follows the 20x launch.
Experts in the loop, you decide
CIPHER GRC never decides for you. Alan AI answers compliance questions, Traverge FedRAMP experts back you up, and you approve, revise, or decline.
A full program, a fraction of the cost
The platform plus Traverge SME support replaces the need to staff a FedRAMP analyst and engineer, with steady, continuous coverage.
Real people, in the loop on your program
CIPHER GRC does the heavy lifting. Traverge FedRAMP experts stay beside your team, so you are never deciding alone.

You decide
CIPHER GRC and Alan AI bring you the evidence and a clear recommendation. You approve, revise, or decline.

Experts beside you
Alan AI answers compliance questions. Traverge FedRAMP experts back you up when you need more than an answer.

Time for your product
You build and sell your service and spend your time on your product and your reputation, while CIPHER GRC and Traverge keep it compliant.

You stay the decision maker.
CIPHER GRC puts the evidence and a clear recommendation in front of you, and you approve, revise, or decline. Alan AI explains and drafts, and when you need more than Alan AI, Traverge FedRAMP subject matter experts are your humans in the loop.
Five pilot partners. Special pricing. Direct access to the people who built it.
We are opening CIPHER GRC to five cloud service providers as pilot partners. You get special pricing and a direct line to the team behind the platform, and your program helps shape what we build next.
What providers ask us first
Is CIPHER GRC itself FedRAMP authorized?
Not yet. CIPHER GRC is working toward FedRAMP Class C Certification, projected for the end of the first quarter of 2027. We run our own program on CIPHER GRC, the same way you will.
Which clouds does it work with?
CIPHER GRC reads your environment with read-only access and works with the major cloud providers. Scan results come in from the scanners you already use, in the formats they produce.
Does Alan make compliance decisions?
No. Alan answers, drafts and recommends. Whether a requirement is met is decided by fixed rules, and every approval is made by a person on your team.
We are already authorized under Rev. 5. Where do we start?
On the 20x track, like every customer. That puts the vulnerability rules due on 7 December 2026 and the other immediate CR26 requirements in place first. Rev. 5 package support is in development and follows the 20x launch.
Is this software only?
No. Every license includes a dedicated Customer Success Analyst and a dedicated Customer Success Engineer from Traverge, alongside the platform and Alan.
Where does our trust center live?
At an address reserved for your company, such as acme.trust.ciphergrc.ai, or on your own domain by pointing a CNAME record at it. You choose what is published and which agencies can see it.
Where is our data kept?
In an instance dedicated to your company, encrypted with managed keys. It is not shared with other customers and is not used to train AI models.
Book a 30-minute program review
Tell us about your cloud service and where you are with FedRAMP. A real person will get back to you, and you will leave the call knowing where your program stands against CR26.

Prefer to talk now? (904) 257-6192 or contact@traverge.com
Thank you for your inquiry.
Your message has been sent. Someone from our team will get back to you shortly.
Need us sooner? Call (904) 257-6192.

Jon Riddle
CEO and Founder, Traverge
Designer of CIPHER GRC
“Federal compliance stifles innovation. A FedRAMP PMO certification only gets your foot in the door. The real challenge is agency authorization, where apprehension creates a costly disconnect. I built CIPHER GRC to bridge that gap so your team can stay focused on innovating market-leading software.”
Designed by Jon Riddle, who has worked in FedRAMP since the program began.
CIPHER GRC was not designed by a committee or handed to a product team as a requirements list. Jon designed it from fifteen years of doing the work: as a cloud service provider's program manager on one side of the authorization boundary, and as a FedRAMP Certified Lead Assessor on the other. Every screen answers a problem he has lived.
A CISSP, Jon has led assessments and advisory work for mission-critical systems at DHS/ICE, DoD and US SOCOM, the Department of Veterans Affairs, the FBI, the FAA, the Federal Trade Commission, and NIH.
Before cybersecurity, Jon was a paratrooper and Airborne Infantryman with the 82nd Airborne Division. The same discipline carries into this work: be ready, own the mission, and take care of the people counting on you.